Pre-Winter Sale - 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: dm70dm

NSE5_FSW_AD-7.6 Fortinet NSE 5 - FortiSwitch 7.6 Administrator Questions and Answers

Questions 4

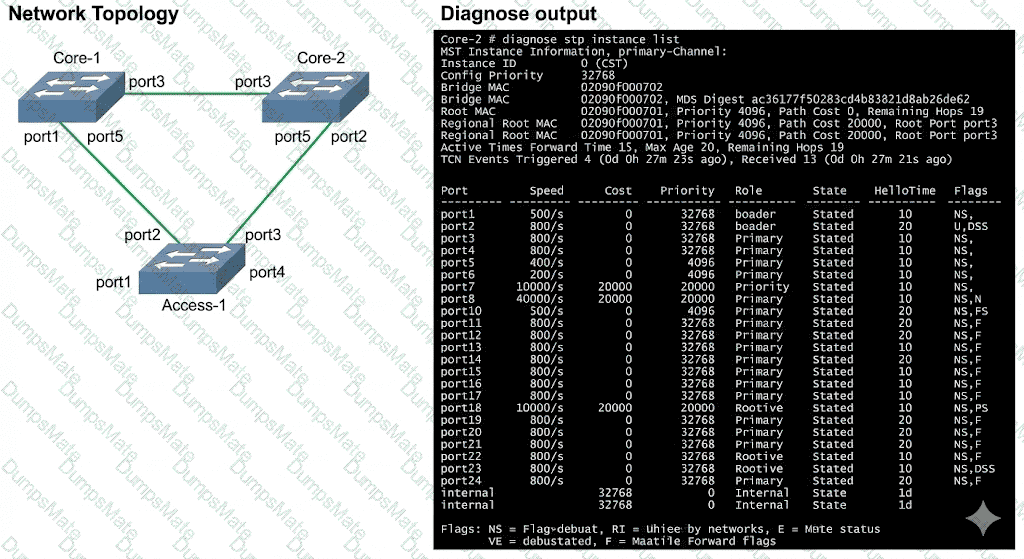
Refer to the exhibits.

NSE5_FSW_AD-7.6 Question 4

Three FortiSwitch devices in standalone mode are interconnected. The CLI command diagnose stp instance list is executed on Core-2. Based on the output shown in the exhibit, what can you conclude about Core-2? (Choose one answer)

Options:

A.

Core-2 has received Bridge Protocol Data Unit (BPDU) from the root bridge.

B.

Core-2 is the designated bridge for all VLANs.

C.

Core-2 is blocking all ports in the Spanning Tree Protocol (STP) topology.

D.

Core-2 provides an alternate path to the root bridge.

Buy Now
Questions 5

(Full question statement start from here)

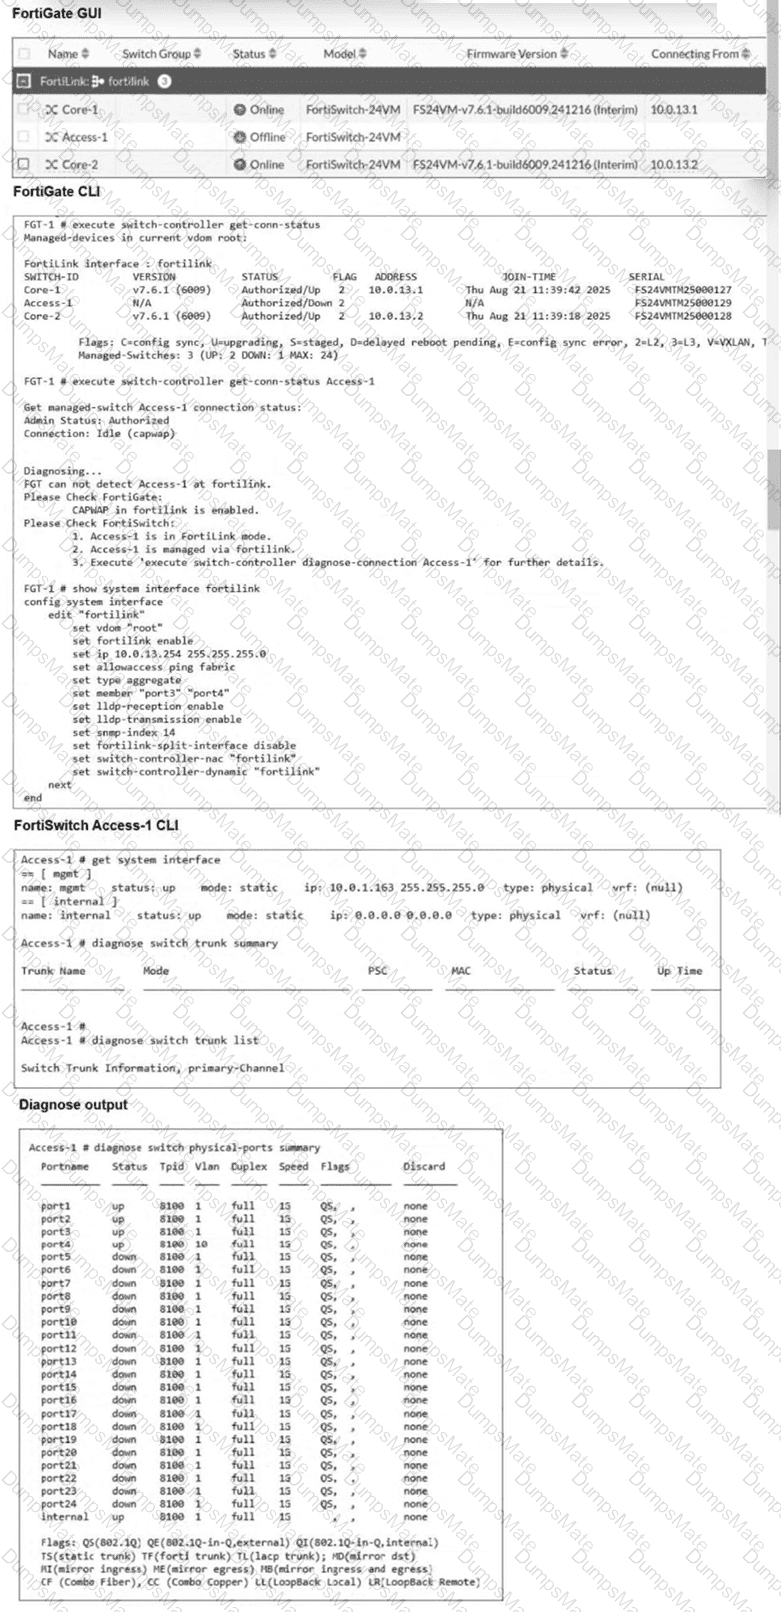
Refer to the exhibits.

NSE5_FSW_AD-7.6 Question 5

Three FortiSwitch devices were recently configured to be managed by FortiGate. Two are managed successfully, butFortiSwitch Access-1is not.

Based on the configuration output, whichinitial changeis required for FortiSwitch Access-1 to be managed? (Choose one answer)

Options:

A.

Assign a static IP on FortiSwitch Access-1.

B.

Change its Control and Provisioning of Wireless Access Points (CAPWAP) settings.

C.

Set Access-1 internal interface mode to DHCP.

D.

Change the NTP server.

Buy Now

NSE5_FSW_AD-7.6 Report Card

Questions 6

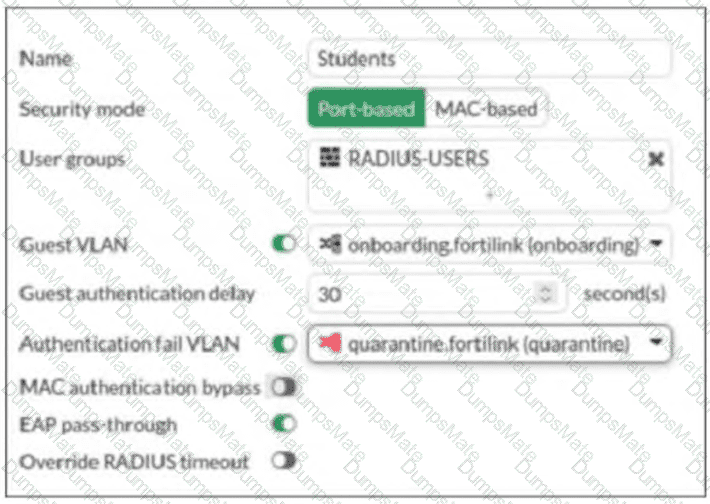
Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 6

The security port policy is configured as shown in the exhibit. Which behavior occurs if a device connected to the port that does not support 802.1X? (Choose one answer)

Options:

A.

The device is blocked from accessing the network.

B.

The device is placed into the onboarding VLAN.

C.

The device is placed into the quarantine VLAN.

D.

The device is assigned to the default management VLAN.

Buy Now
Questions 7

How does FortiGate handle configuration of flow tracking sampling if you export the settings to a managed FortiSwitch stack with sampling mode set to perimeter is true?

Options:

A.

FortiGate configures FortiSwitch to perform ingress sampling on all switch interfaces.

B.

FortiGate configures FortiSwitch to perform ingress sampling on all switch interfaces, except ICL and ISL interfaces.

C.

FortiGate configures and enables flow sampling on FortiSwitch but does not change existing sampling settings of interfaces.

D.

FortiGate configures and enables egress sampling on all management interfaces.

Buy Now
Questions 8

Which three are valid actions that a FortiSwitch access control list (ACL) can apply to matching traffic? (Choose three answers)

Options:

A.

Assign the VLAN ID

B.

Quarantine devices

C.

Traffic processing

D.

Set outer VLAN tags

E.

QoS

Buy Now
Questions 9

You are deploying a new FortiSwitch device in a branch office and you want it to be automatically detected and managed by FortiGate. Which FortiSwitch feature enables automatic detection during deployment? (Choose one answer)

Options:

A.

Zero-touch deployment

B.

Auto-discovery

C.

Link Layer Discovery Protocol (LLDP)

D.

FortiLink heartbeat

Buy Now
Questions 10

(Full question statement start from here)

You are planning to deploy FortiSwitch devices on your network. Your goal is to simplify management and ensure integration with the Security Fabric. Which deployment approach should you choose? (Choose one answer)

Options:

A.

Use the FortiSwitch-Manager device for centralized management.

B.

Manage FortiSwitch from FortiManager for large-scale enterprise deployments.

C.

Use FortiEdge Cloud for centralized management with advanced analytics.

D.

Manage FortiSwitch on FortiGate using FortiLink.

Buy Now
Questions 11

(Full question statement start from here)

A FortiGate is connected to a pair of FortiSwitch devices.

For redundancy, FortiGate must use uplinks on both switches simultaneouslywithout depending on Spanning Tree Protocol (STP).

Which configuration is required? (Choose one answer)

Options:

A.

Multi-tier topology

B.

Multichassis link aggregation group (MCLAG)

C.

Full mesh high availability (HA)

D.

Link aggregation group (LAG)

Buy Now
Questions 12

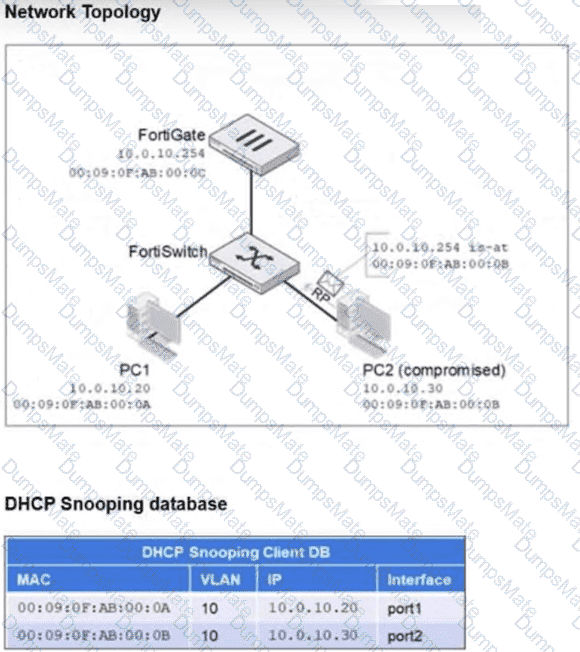
Refer to the exhibits.

NSE5_FSW_AD-7.6 Question 12

All three FortiSwitch-connected ports are configured in VLAN 10. FortiGate acts as the Dynamic Host Configuration Protocol (DHCP) server and is connected to a DHCP snooping trusted trunk port. PC1 and PC2 are connected to ports configured as untrusted for Dynamic ARP Inspection (DAI), and no static bindings are configured in the IP source guard (IPSG) database. PC2 is compromised and attempts to spoof the FortiGate IP address by sending forged Address Resolution Protocol (ARP) replies with its own MAC address. What will FortiSwitch do with the ARP packets from PC2? (Choose one answer)

Options:

A.

Forward the ARP replies because there are no IPSG bindings blocking them.

B.

Accept the ARP replies because the VLAN has DAI enabled and FortiGate is a trusted DHCP server.

C.

Forward the ARP replies to all VLAN 10 ports because DAI is only active on trusted ports.

D.

Drop the ARP replies because they fail DAI validation against the DHCP snooping database.

Buy Now
Questions 13

Which statement about the configuration of VLANs on a managed FortiSwitch port is true?

Options:

A.

Untagged VLANs must be part of the allowed VLANs: ingress and egress.

B.

FortiSwitch VLAN interfaces are created only when FortiSwitch is managed by Forti-Gate.

C.

The native VLAN is implicitly part of the allowed VLAN on the port.

D.

Allowed VLANS expand the collision domain to the port.

Buy Now
Questions 14

What type of multimode transceiver can be used to split a 40G port?

Options:

A.

QSFP+ transceiver

B.

SFP transceiver

C.

QSFP transceiver

D.

SFP+ transceiver

Buy Now
Questions 15

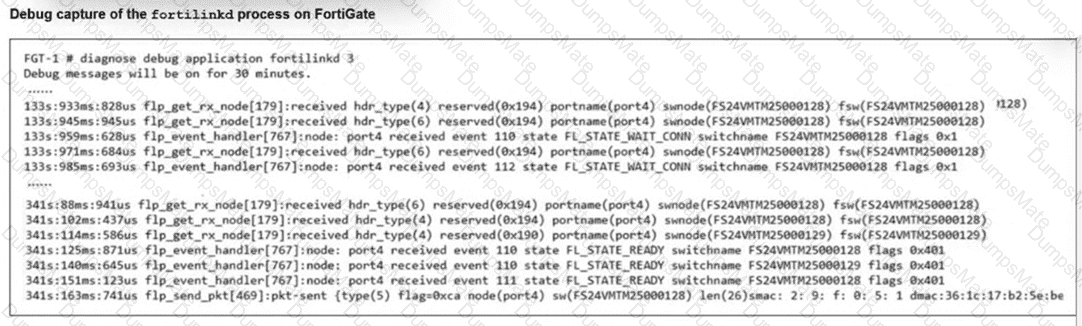
Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 15

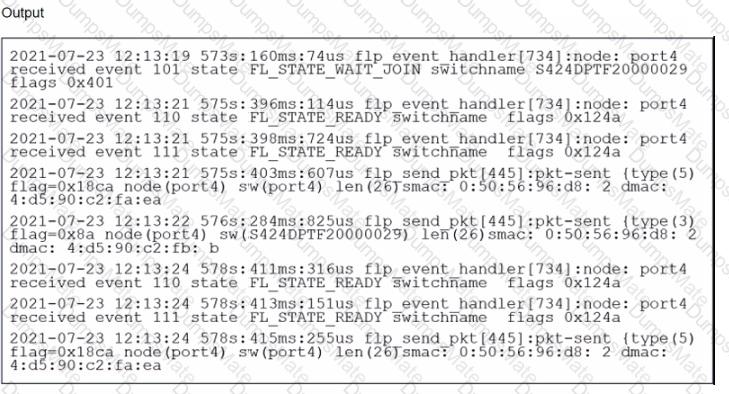
A periodic heartbeat message sent from a managed FortiSwitch and corresponding acknowledgments from FortiGate is shown. What does this behavior indicate? (Choose one answer)

Options:

A.

The FortiLink connection between FortiGate and FortiSwitch is healthy and active.

B.

FortiGate is unable to establish a FortiLink session with FortiSwitch.

C.

FortiSwitch is expecting an authorization from FortiGate.

D.

FortiSwitch has not been authorized yet.

Buy Now
Questions 16

(Full question statement start from here)

What is an advantage of using a FortiSwitch stack in managed switch mode with FortiGate when deploying VLANs? (Choose one answer)

Options:

A.

FortiGate executing the routing and FortiSwitch managing its configuration.

B.

Ensuring VLAN traffic can pass between connected switches in the stack.

C.

FortiGate no longer needing to manage any VLAN configuration.

D.

FortiGate provides visibility and control for inter-vlan traffic.

Buy Now
Questions 17

In which two ways can you assign a FortiSwitch port to a VDOM using multi-tenancy setup? (Choose two.)

Options:

A.

Switch the FortiLink interface to the target VDOM.

B.

Remove the managed FortiSwitch and allocate ports directly on FortiSwitch.

C.

Create a virtual port pool on the FortiGate CLI.

D.

Assign a port to a VDOM directly on the managed FortiSwitch.

Buy Now
Questions 18

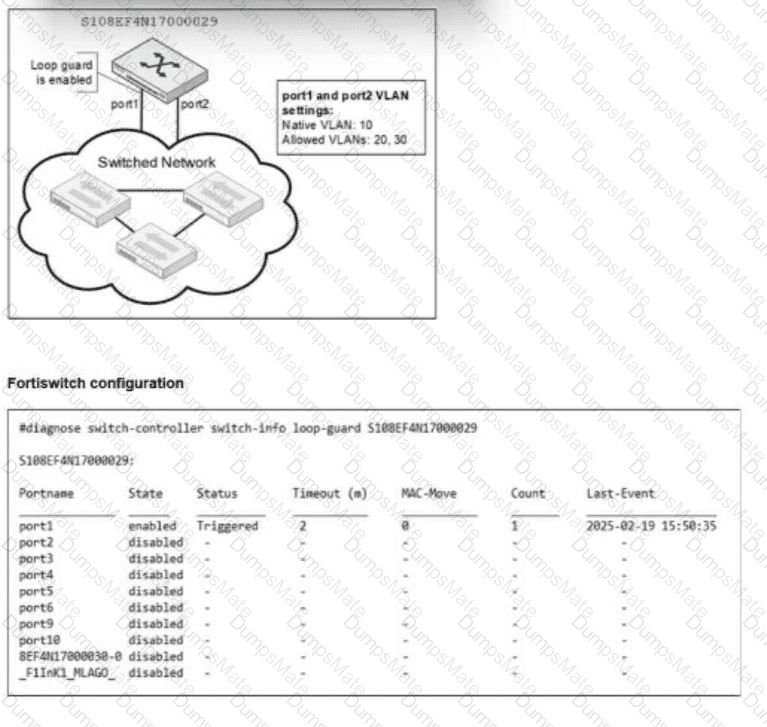
Refer to the exhibits.

NSE5_FSW_AD-7.6 Question 18

You are reviewing a FortiSwitch configuration where port1 and port2 are connected to a switched network. Loop guard is enabled on port1.

The CLI output shows that the port1 status is triggered due to loop guard. Which two conditions could have caused this shutdown? (Choose two.)

Options:

A.

A loop guard frame sent from port1 is received on port2.

B.

A loop guard frame sent from port1 is received back on port1.

C.

Loop guard is triggered because port2 did not send any bridge protocol data units (BPDU).

D.

Loop guard is triggered because the port detected excessive traffic.

Buy Now
Questions 19

Which statement about the quarantine VLAN on FortiSwitch is true?

Options:

A.

Quarantine VLAN has no DHCP server

B.

Users who fail 802.1X authentication can be placed on the quarantine VLAN.

C.

It is only used for quarantined devices if global setting is set to quarantine by VLAN.

D.

FortiSwitch can block devices without configuring quarantine VLAN to be part of the allowed VLANs.

Buy Now
Questions 20

Which is a requirement to enable SNMP v2c on a managed FortiSwitch?

Options:

A.

Create an SNMP user to use for authentication and encryption.

B.

Specify an SNMP host to send traps to.

C.

Enable an SNMP v3 to handle traps messages with SNMP hosts.

D.

Configure SNMP agent and communities.

Buy Now
Questions 21

Exhibit.

LAG and MCLAG are used to increase the available network bandwidth and enable redundancy. How does spanning tree protocol see MCLAG and LAG if they are configured based on the physi-cal view shown in the exhibit? (Choose two)

Options:

A.

Switch 1. Switch 2, and Switch 3 are seen as one MCLAG peer group

B.

Switch 3 and Switch 4 uplinks are treated as single interfaces.

C.

Switch 3 and switch 4 are seen as one MCLAG switch client

D.

Switch 1 and Switch 2 both seen as one single switch.

Buy Now
Questions 22

What can an administrator do to maintain a FortiGate-compatible FortiSwitch configuration when changing the management mode from standalone to FortiLinK?

Options:

A.

Use a migration tool based on Python script to convert the configuration.

B.

Enable the FortiLink setting on FortiSwitch before the authorization process.

C.

FortiGate automatically saves the existing FortiSwitch configuration during the FortiLink management process.

D.

Register FortiSwitch to FortiSwitch Cloud to save a copy before managing with FortiGate.

Buy Now
Questions 23

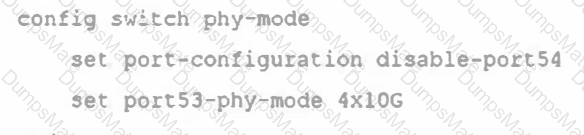
Exhibit.

NSE5_FSW_AD-7.6 Question 23

What conditions does a FortiSwitch need to have to successfully configure the options shown in the exhibit above? (Choose two.)

Options:

A.

The FortiSwitch model is equipped with a maximum of 54 interfaces.

B.

The CLI commands are enabling a splitpo rt into four 10Gbps interfaces.

C.

The port full speed prior the split was 100G SFP+

D.

The split port can be assigned to native VLAN

Buy Now
Questions 24

Which two statements about VLAN assignments on FortiSwitch ports are true? (Choose two.)

Options:

A.

Configure a native VLAN on the FortiLink

B.

Assign an IP address and subnet mask to FortiSwitch VLANs

C.

Only assign one native VLAN on a port

D.

Assign untagged VLANs using FortiGate CLI

Buy Now
Questions 25

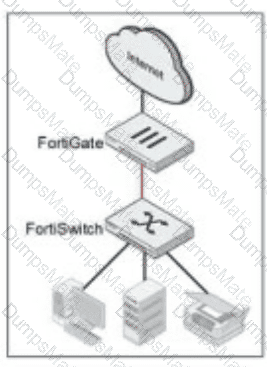
Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 25

Which two configurations can you use for the FortiLink interface in a basic single FortiGate-single FortiSwitch topology? (Choose two.)

Options:

A.

Single physical port

B.

Port channel

C.

Switchport mode trunk

D.

Link aggregation group (LAG)

Buy Now
Questions 26

Which Ethernet frame can create Layer 2 flooding due to all bytes on the destination MAC address being set to all FF?

Options:

A.

The broadcast Ethernet frame

B.

The unicast Ethernet frame

C.

The multicast Ethernet frame

D.

The anycast Ethernet frame

Buy Now
Questions 27

Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 27

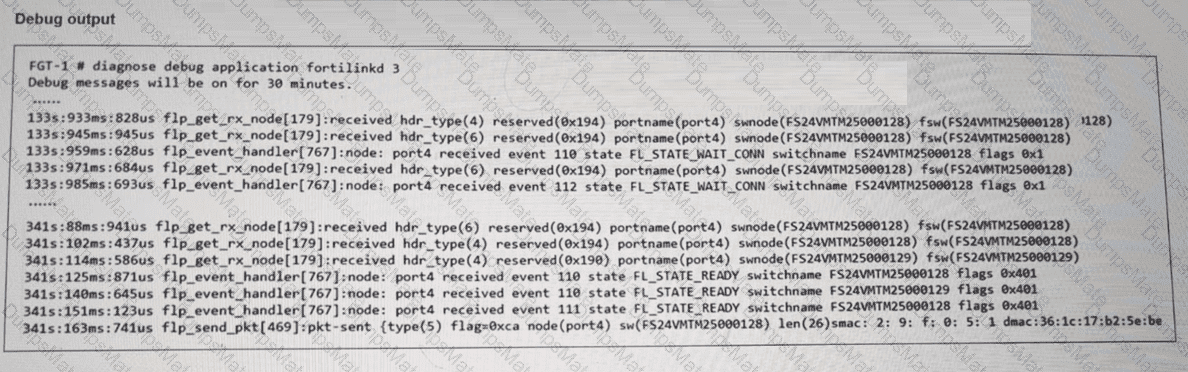
Which two statements best describe what is displayed in the FortiLink debug output shown in the exhibit? (Choose two.)

Options:

A.

FortiSwitch is sending FortiLink heartbeats to FortiGate.

B.

FortiSwitch is discovered and authorized by FortiGate.

C.

FortiSwitch is in a waiting state to join the stack group on FortiGate.

D.

FortiSwitch is ready to push its new hostname to FortiGate.

Buy Now
Questions 28

Which two types of Layer 3 interfaces can participate in dynamic routing on FortiSwitch? (Choose two.)

Options:

A.

Detected management interfaces

B.

Loopback interfaces

C.

Switch virtual interfaces

D.

Physical interfaces

Buy Now
Questions 29

Which two statements about the FortiLink authorization process are true? (Choose two.)

Options:

A.

The administrator must manually pre-authorize FortiGate on FortiSwitch by adding the FortiGate serial number.

B.

FortiSwitch requires a reboot to complete the authorization process.

C.

A FortiLink frame is sent by FortiGate to FortiSwitch to complete the authorization.

D.

FortiLink authorization sets the FortiSwitch management mode to FortiLink.

Buy Now
Questions 30

Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 30

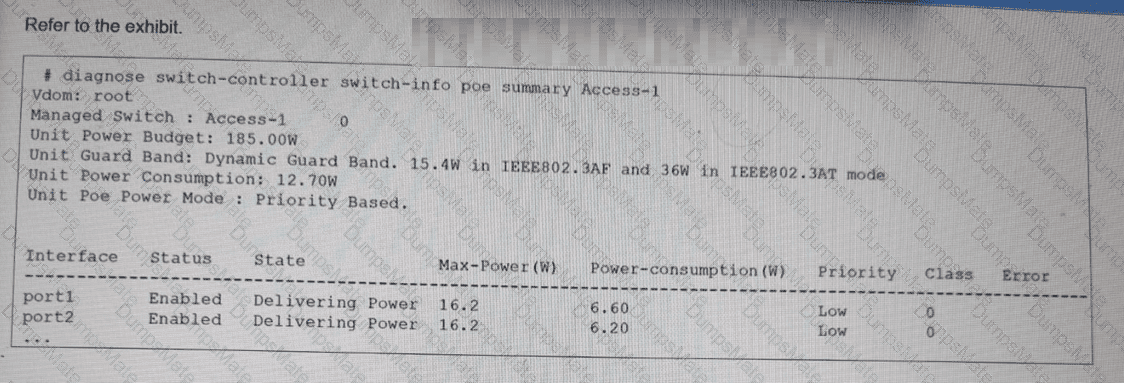
The FortiSwitch CLI output of the diagnose switch-controller switch-info poe summary command for the switch Access-1 is shown. It shows that two ports have Power over Ethernet (PoE) enabled and are already in use. What is the most important consideration if you want to connect additional PoE devices to FortiSwitch? (Choose one answer)

Options:

A.

All plugged devices use the same PoE standard: 802.3af/at.

B.

The FortiSwitch model supports the number of PoE devices that you want to connect.

C.

The PoE power mode matches the PoE standard of the device.

D.

The total PoE consumption must not exceed the FortiSwitch power budget.

Buy Now
Questions 31

Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 31

You have just authorized a new FortiSwitch on your FortiGate, and it appears online in the GUI. To verify that FortiLink connectivity is healthy, what should you check next? (Choose one answer)

Options:

A.

Check that the switch automatically disables all unused ports.

B.

Look for FortiLink heartbeat messages sent from FortiSwitch to FortiGate every few seconds and confirm FortiGate acknowledges them.

C.

Verify that FortiGate has pushed a new firmware image to FortiSwitch immediately.

D.

Ensure the FortiSwitch is automatically sending log events to FortiAnalyzer.

Buy Now
Questions 32

What can an administrator do to maintain the existing standalone FortlSwltch configuration while changing the management mode to FortLink?

Options:

A.

Use a migration tool based on python script to convert the configuration

B.

Enable the Forti-link setting on FortiSwitch before the authorization process

C.

FortiGate will automatically save the existing FortiSwitch configuration during the Forti-link management process.

D.

Register FortiSwitch to For1ISwitch Cloud to save a copy before managing by Forti-Gate.

Buy Now
Questions 33

An administrator needs to deploy managed FortiSwitch devices in a remote location where multiple VLANs must be utilized to segment devices. No Layer 3 switch or router is present. The the only WAN connectivity is the router provided by the ISP connected to the public internet.

Which two items will the administrator need to use? (Choose two.)

Options:

A.

A FortiSwitch interface connected to the ISP router configured with fortilink-13-mode enabled.

B.

FortiSwitch and FortiGate devices configured with VXLAN interfaces.

C.

FortiSwitch devices configured with NAT disabled.

D.

FortiSwitch devices that have the required internal hardware for this configuration.

E.

FortiSwitch and FortiGate devices configured with IPsec interfaces.

Buy Now
Questions 34

How is traffic routed on FortiSwitch?

Options:

A.

Hardware-based routing on FortiSwitch is handled by the CPU.

B.

FortiSwitch looks up the hardware routing table and then the forwarding information base (FIB).

C.

ASIC hardware routing can only handle dynamic routing, if supported.

D.

Layer 3 routing can be configured on FortiSwitch, while managed by FortiGate.

Buy Now
Exam Code: NSE5_FSW_AD-7.6
Exam Name: Fortinet NSE 5 - FortiSwitch 7.6 Administrator
Last Update: Sep 16, 2026
Questions: 114

PDF + Testing Engine

$49.5  $164.99

Testing Engine

$37.5  $124.99
buy now NSE5_FSW_AD-7.6 testing engine

PDF (Q&A)

$31.5  $104.99
buy now NSE5_FSW_AD-7.6 pdf
dumpsmate guaranteed to pass

24/7 Customer Support

DumpsMate's team of experts is always available to respond your queries on exam preparation. Get professional answers on any topic of the certification syllabus. Our experts will thoroughly satisfy you.

Site Secure

mcafee secure

TESTED 17 Sep 2026