Pre-Winter Sale - 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: dm70dm

SC-100 Microsoft Cybersecurity Architect Questions and Answers

Questions 4

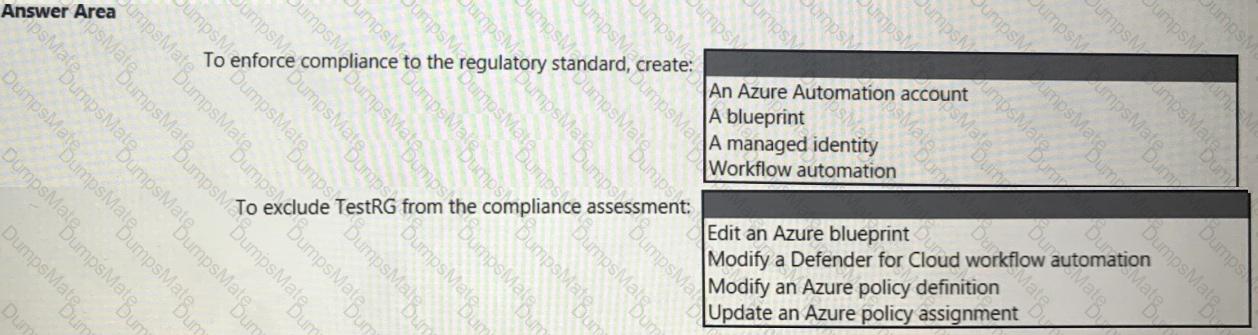
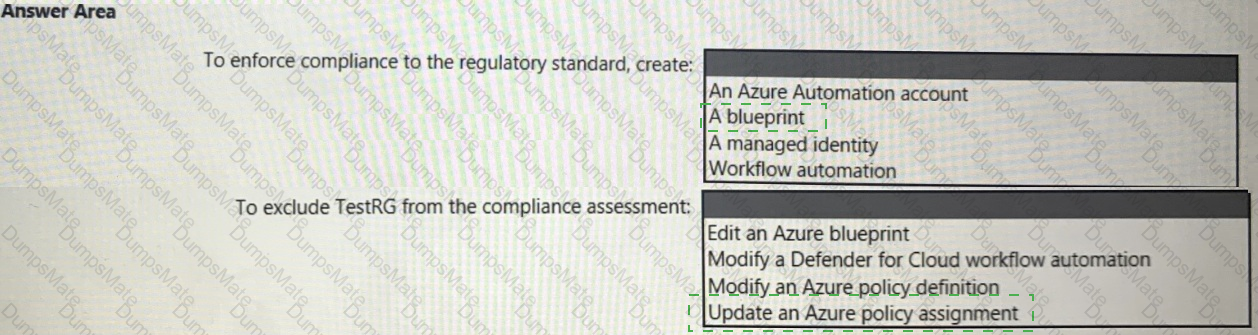
You need to recommend a solution to meet the compliance requirements.

What should you recommend? To answer, select the appropriate options in the answer area.

NOTE: Each correct selection is worth one point.

SC-100 Question 4

Options:

Buy Now
Questions 5

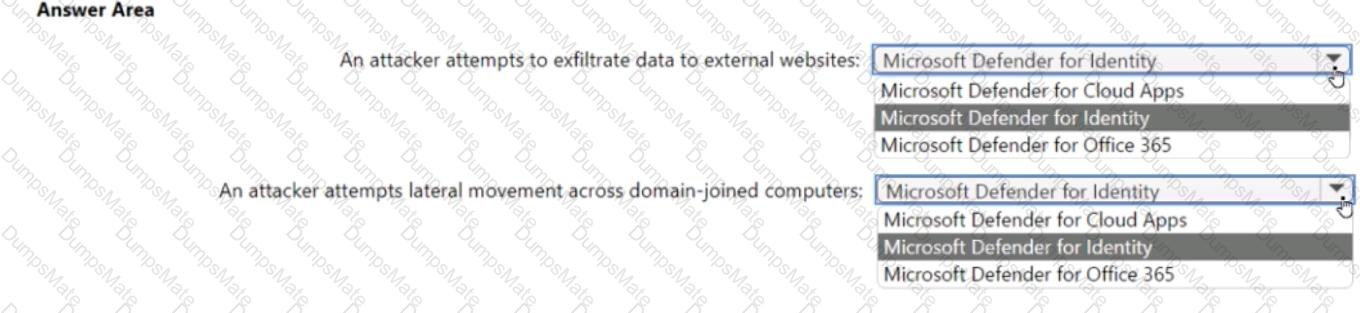
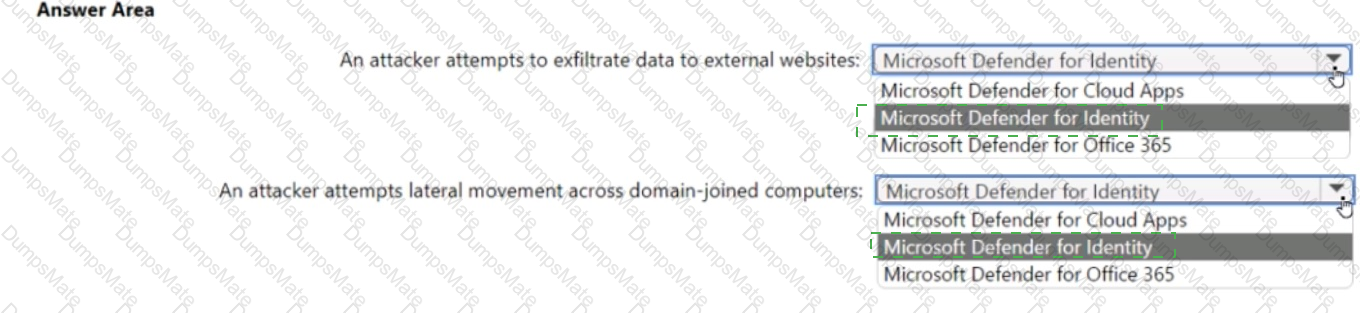
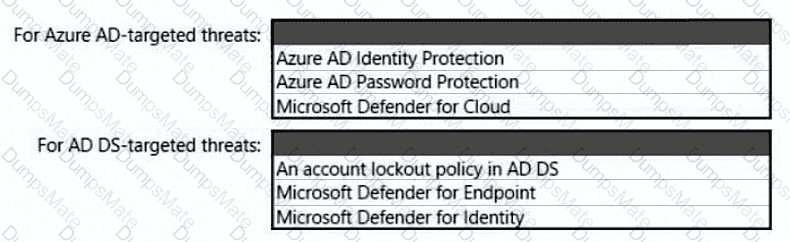
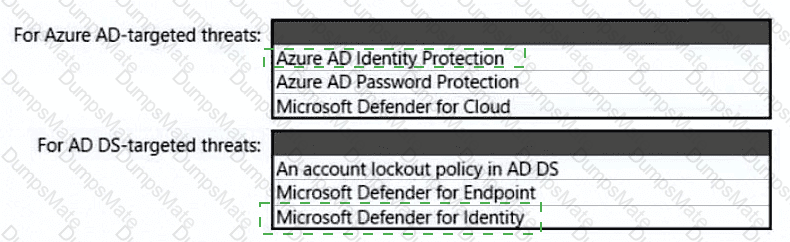
For a Microsoft cloud environment, you are designing a security architecture based on the Microsoft Cybersecurity Reference Architectures (MCRA). You need to protect against the following external threats of an attack chain:

• An attacker attempts to exfiltrate data to external websites.

• An attacker attempts lateral movement across domain-joined computers.

What should you include in the recommendation for each threat? To answer, select the appropriate options in the answer area.

SC-100 Question 5

Options:

Buy Now

SC-100 Report Card

Questions 6

You have a Microsoft 365 tenant.

You have an Azure subscription that contains Azure App Service web apps. The apps have the following characteristics:

• The apps use third-party and open-source components.

• The apps were developed by using C#, Python, and Java.

• The app deployment process is managed by using Azure DevOps.

• The source code for the apps is stored in GitHub Enterprise Cloud repositories and protected by using GitHub Advanced Security.

You need to reduce the risk of supply chain attacks during the application lifecycle.

What should you implement?

Options:

A.

NuGet Audit

B.

secret scanning

C.

Dependabot alerts

D.

app governance in Microsoft Defender for Cloud Apps

Buy Now
Questions 7

Your company is moving all on-premises workloads to Azure and Microsoft 365. You need to design a security orchestration, automation, and response (SOAR) strategy in Microsoft Sentinel that meets the following requirements:

• Minimizes manual intervention by security operation analysts

• Supports Waging alerts within Microsoft Teams channels

What should you include in the strategy?

Options:

A.

data connectors

B.

playbooks

C.

workbooks

D.

KQL

Buy Now
Questions 8

Your company has a Microsoft 365 E5 subscription.

The Chief Compliance Officer plans to enhance privacy management in the working environment. You need to recommend a solution to enhance the privacy management. The solution must meet the following requirements:

• Identify unused personal data and empower users to make smart data handling decisions.

• Provide users with notifications and guidance when a user sends personal data in Microsoft Teams.

• Provide users with recommendations to mitigate privacy risks.

What should you include in the recommendation?

Options:

A.

Microsoft Viva Insights

B.

Advanced eDiscovery

C.

Privacy Risk Management in Microsoft Priva

D.

communication compliance in insider risk management

Buy Now
Questions 9

You have a customer that has a Microsoft 365 subscription and uses the Free edition of Azure Active Directory (Azure AD)

The customer plans to obtain an Azure subscription and provision several Azure resources.

You need to evaluate the customer ' s security environment.

What will necessitate an upgrade from the Azure AD Free edition to the Premium edition?

Options:

A.

role-based authorization

B.

Azure AD Privileged Identity Management (PIM)

C.

resource-based authorization

D.

Azure AD Multi-Factor Authentication

Buy Now
Questions 10

You are designing security for an Azure landing zone. Your company identifies the following compliance and privacy requirements:

• Encrypt cardholder data by using encryption keys managed by the company.

• Encrypt insurance claim files by using encryption keys hosted on-premises.

Which two configurations meet the compliance and privacy requirements? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.

Options:

A.

Store the insurance claim data in Azure Blob storage encrypted by using customer-provided keys.

B.

Store the cardholder data in an Azure SQL database that is encrypted by using keys stored in Azure Key Vault Managed HSM

C.

Store the insurance claim data in Azure Files encrypted by using Azure Key Vault Managed HSM.

D.

Store the cardholder data in an Azure SQL database that is encrypted by using Microsoft-managed Keys.

Buy Now
Questions 11

You plan to deploy 20 Azure Kubernetes Service (AKS) clusters. The cluster configuration will be managed declaratively by using Kubernetes manifest files stored in Azure Repos.

You need to recommend a solution to ensure that the configuration of all the clusters remains consistent by using the manifest files stored in Azure Repos.

What should you include in the recommendation?

Options:

A.

Gatekeeper

B.

Dependency Tracker

C.

Dependency

D.

Flux

Buy Now
Questions 12

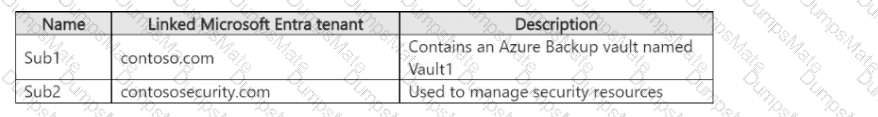
You have the Azure subscriptions shown in the following table.

SC-100 Question 12

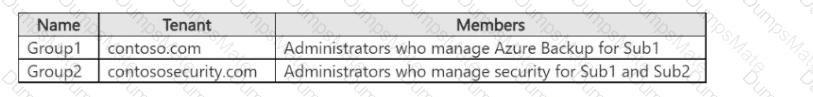
The tenants contain the groups shown in the following table.

SC-100 Question 12

You perform the following actions:

• Configure multi-user authorization (MUA) for Vault1 by using a resource guard deployed to Sub2.

• Enable all available MUA controls for Vault1.

• In contoso.com, create a Privileged Identity Management (PIM) assignment named Assignment1.

• Configure Assignment1 to enable Group! to activate the Contributor role for Vault1.

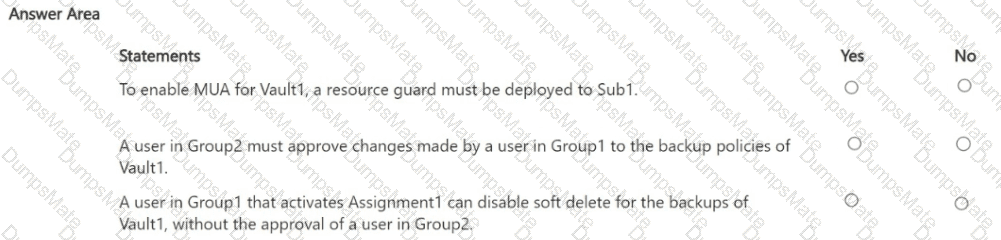
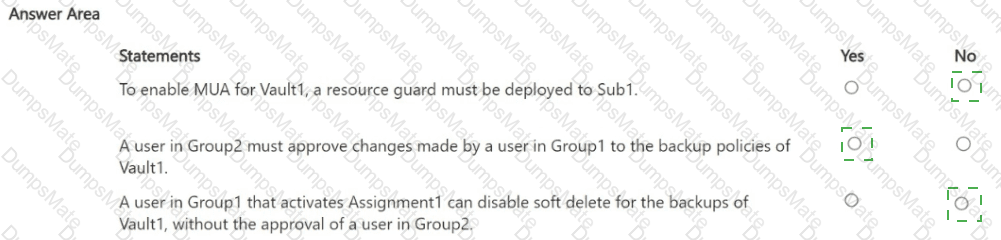
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.

SC-100 Question 12

Options:

Buy Now
Questions 13

Your on-premises network contains an Active Directory Domain Services (AD DS) domain named corpxontoso.com and an AD DS-integrated application named App1.

Your perimeter network contains a server named Server1 that runs Windows Server.

You have a Microsoft Entra tenant named contoso.com that syncs with corp.contoso.com.

You plan to implement a security solution that will include the following configurations:

• Manage access to App1 by using Microsoft Entra Private Access.

• Deploy a Microsoft Entra application proxy connector to Server1.

• Implement single sign-on (SSO) for App1 by using Kerberos constrained delegation.

• For Server1, configure the following rules in Windows Defender Firewall with Advanced Security:

o Rule1: Allow TCP 443 inbound from a designated set of Azure URLs.

o Rule2: Allow TCP 443 outbound to a designated set of Azure URLs.

o Rule3: Allow TCP 80 outbound to a designated set of Azure URLs.

o Rule4: Allow TCP 389 outbound to the domain controllers on corp.contoso.com.

You need to maximize security for the planned implementation. The solution must minimize the impact on the connector.

Which rule should you remove?
Options:

A.

Rule1

B.

Rule2

C.

Rule3

D.

Rule4

Buy Now
Questions 14

You have a Microsoft Entra tenant named contoso.com.

You have a partner company that has a multi-tenant application named App1. App1 is registered to a Microsoft Entra tenant named fabnkam.com.

You need to ensure that the users in contoso.com can authenticate to App1.

What should you recommend creating in contoso.com?

Options:

A.

a service principal

B.

a system-assigned managed identity

C.

an application object

D.

a user-assigned managed identity

Buy Now
Questions 15

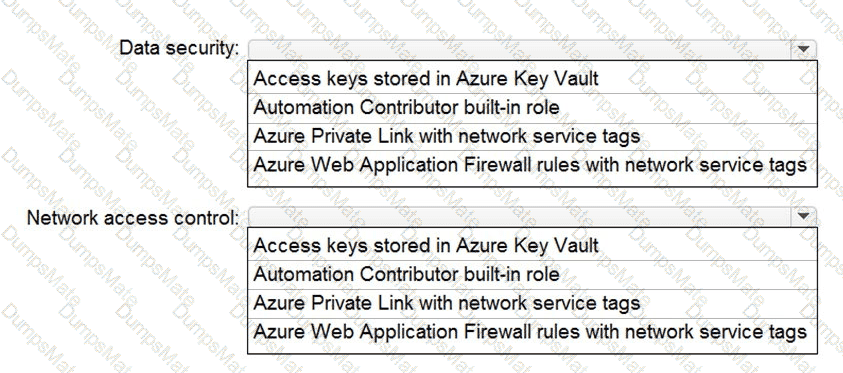
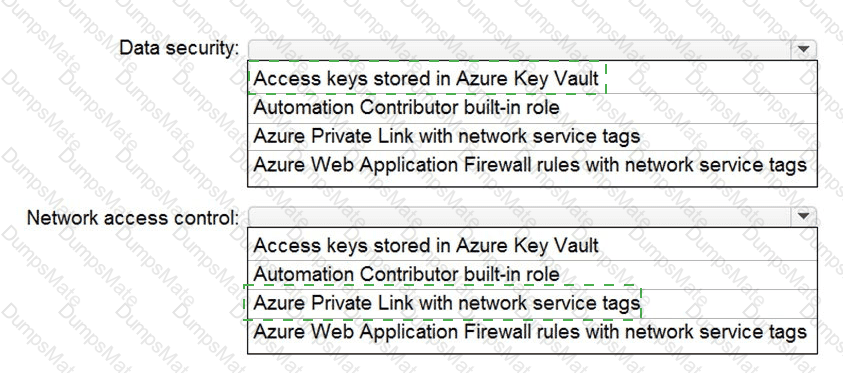
You are designing security for a runbook in an Azure Automation account. The runbook will copy data to Azure Data Lake Storage Gen2.

You need to recommend a solution to secure the components of the copy process.

What should you include in the recommendation for each component? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.

SC-100 Question 15

Options:

Buy Now
Questions 16

You have an Azure AD tenant that syncs with an Active Directory Domain Services (AD DS) domain.

You have an on-premises datacenter that contains 100 servers. The servers run Windows Server and are backed up by using Microsoft Azure Backup Server (MABS).

You are designing a recovery solution for ransomware attacks. The solution follows Microsoft Security Best Practices.

You need to ensure that a compromised administrator account cannot be used to delete the backups

What should you do?

Options:

A.

From a Recovery Services vault generate a security PIN for critical operations.

B.

From Azure Backup, configure multi-user authorization by using Resource Guard.

C.

From Microsoft Azure Backup Setup, register MABS with a Recovery Services vault

D.

From Azure AD Privileged Identity Management (PIM), create a role assignment for the Backup Contributor role.

Buy Now
Questions 17

Your company has a main office and 10 branch offices. Each branch office contains an on-premises file server that runs Windows Server and multiple devices that run either Windows 11 or macOS. The devices are enrolled in Microsoft Intune.

You have a Microsoft Entra tenant.

You need to deploy Global Secure Access to implement web filtering for device traffic to the internet The solution must ensure that all the web traffic from the devices in the branch offices is controlled by using Global Secure Access.

What should you do first in each branch office?

Options:

A.

Configure an Intune policy to deploy the Global Secure Access client to each device.

B.

Configure an IPsec tunnel on the router.

C.

Install the Microsoft Entra private network connector on the file server.

D.

Configure an Intune policy to onboard Microsoft Defender for Endpoint to each device.

Buy Now
Questions 18

You are designing the security standards for containerized applications onboarded to Azure. You are evaluating the use of Microsoft Defender for Containers.

In which two environments can you use Defender for Containers to scan for known vulnerabilities? Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.

Options:

A.

Linux containers deployed to Azure Container Registry

B.

Linux containers deployed to Azure Kubernetes Service (AKS)

C.

Windows containers deployed to Azure Container Registry

D.

Windows containers deployed to Azure Kubernetes Service (AKS)

E.

Linux containers deployed to Azure Container Instances

Buy Now
Questions 19

Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.

After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.

You have an Azure subscription that has Microsoft Defender for Cloud enabled.

You are evaluating the Azure Security Benchmark V3 report.

In the Secure management ports controls, you discover that you have 0 out of a potential 8 points.

You need to recommend configurations to increase the score of the Secure management ports controls.

Solution: You recommend enabling the VM Access extension on all virtual machines.

Does this meet the goal?

Options:

A.

Yes

B.

No

Buy Now
Questions 20

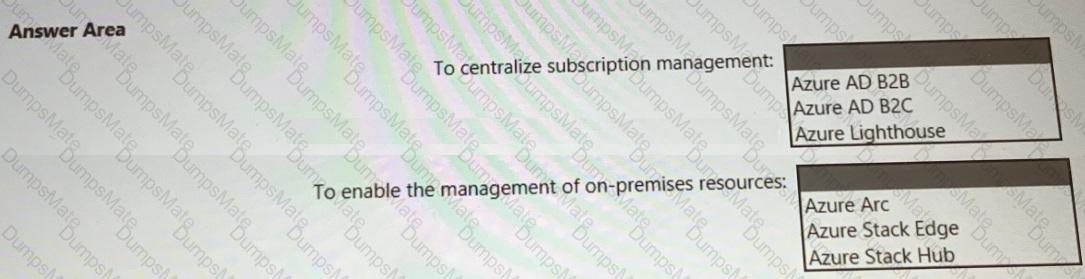
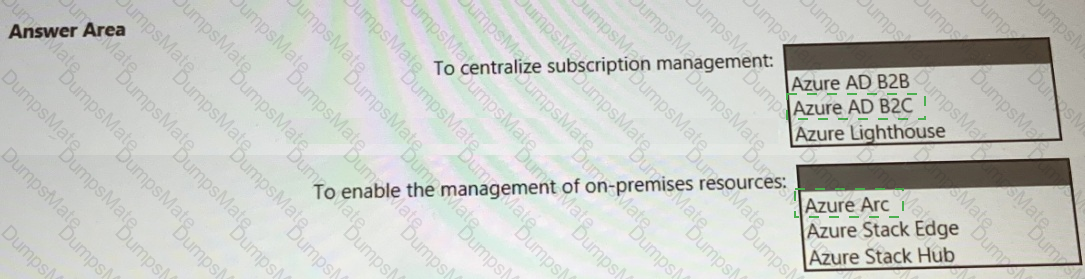
You need to recommend a multi-tenant and hybrid security solution that meets to the business requirements and the hybrid requirements. What should you recommend? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.

SC-100 Question 20

Options:

Buy Now
Questions 21

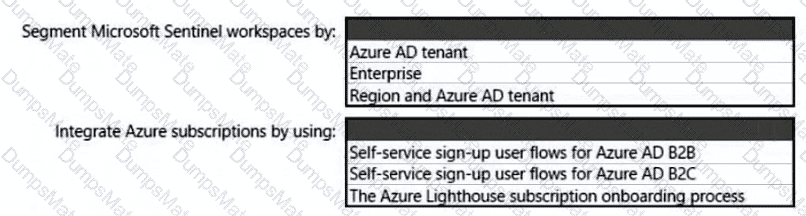
You need to recommend a strategy for securing the litware.com forest. The solution must meet the identity requirements. What should you include in the recommendation? To answer, select the appropriate options in the answer area. NOTE; Each correct selection is worth one point.

SC-100 Question 21

Options:

Buy Now
Questions 22

You need to design a strategy for securing the SharePoint Online and Exchange Online data. The solution must meet the application security requirements.

Which two services should you leverage in the strategy? Each correct answer presents part of the solution. NOTE; Each correct selection is worth one point.

Options:

A.

Azure AD Conditional Access

B.

Microsoft Defender for Cloud Apps

C.

Microsoft Defender for Cloud

D.

Microsoft Defender for Endpoint

E.

access reviews in Azure AD

Buy Now
Questions 23

You need to recommend a solution for securing the landing zones. The solution must meet the landing zone requirements and the business requirements.

What should you configure for each landing zone?

Options:

A.

Azure DDoS Protection Standard

B.

an Azure Private DNS zone

C.

Microsoft Defender for Cloud

D.

an ExpressRoute gateway

Buy Now
Questions 24

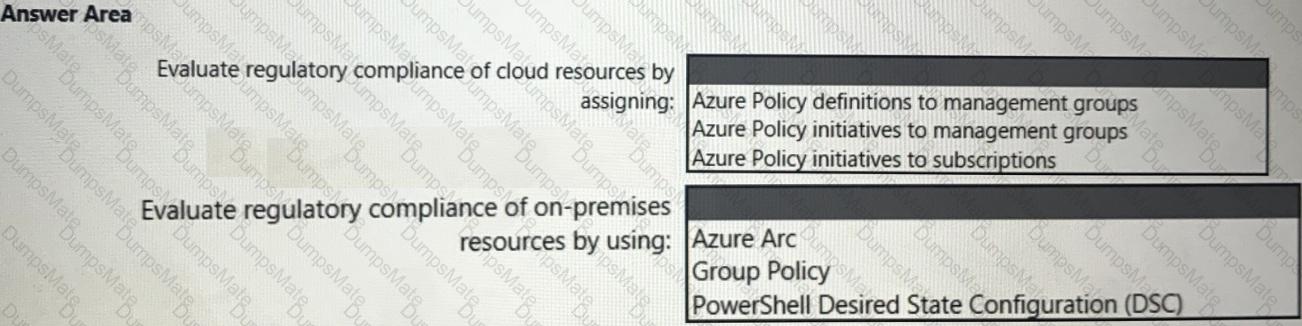
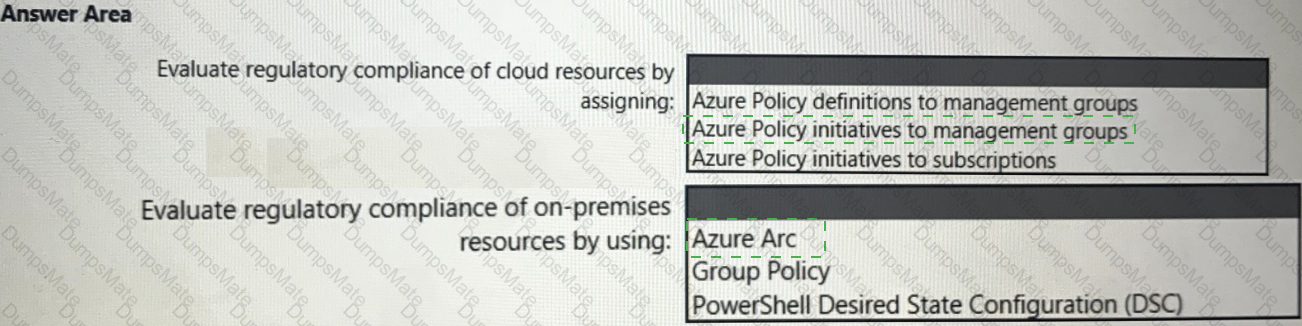
You need to recommend a solution to evaluate regulatory compliance across the entire managed environment. The solution must meet the regulatory compliance requirements and the business requirements.

What should you recommend? To answer, select the appropriate options in the answer area.

NOTE: Each correct selection is worth one point.

SC-100 Question 24

Options:

Buy Now
Questions 25

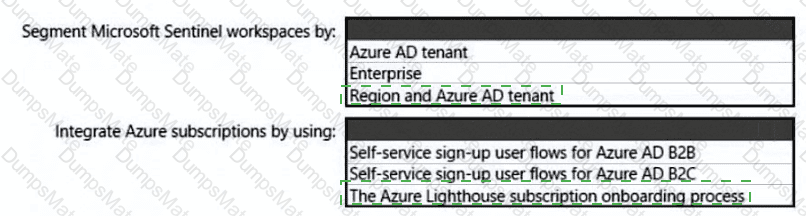
You need to recommend a SIEM and SOAR strategy that meets the hybrid requirements, the Microsoft Sentinel requirements, and the regulatory compliance requirements.

What should you recommend? To answer, select the appropriate options in the answer area.

NOTE: Each correct selection is worth one point.

SC-100 Question 25

Options:

Buy Now
Questions 26

To meet the application security requirements, which two authentication methods must the applications support? Each correct answer presents a complete solution.

NOTE: Each correct selection is worth one point.

Options:

A.

Security Assertion Markup Language (SAML)

B.

NTLMv2

C.

certificate-based authentication

D.

Kerberos

Buy Now
Questions 27

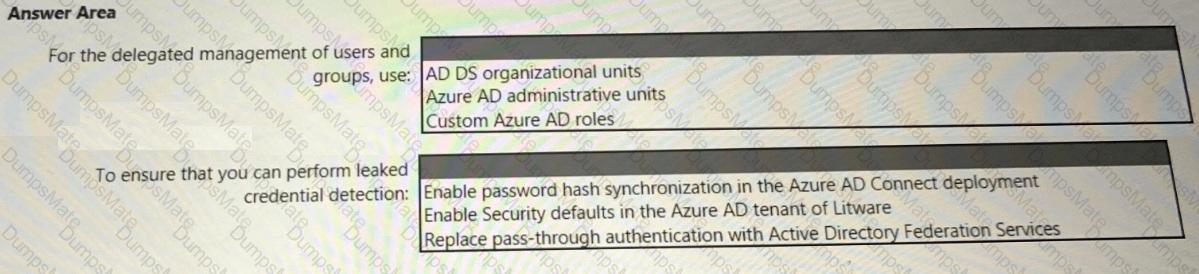
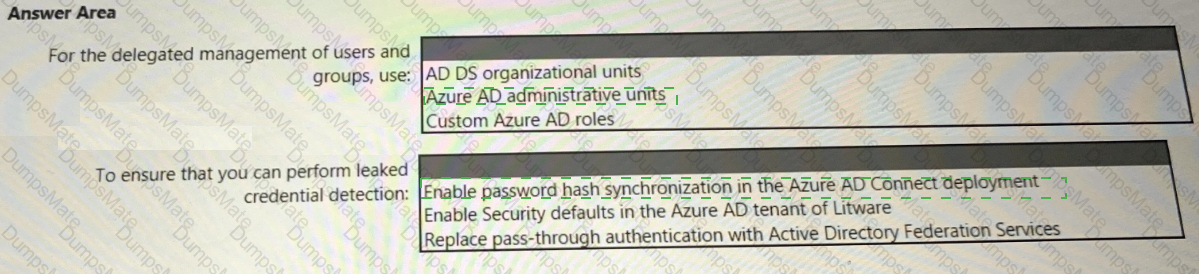
You need to recommend an identity security solution for the Azure AD tenant of Litware. The solution must meet the identity requirements and the regulatory compliance requirements.

What should you recommend? To answer, select the appropriate options in the answer area.

NOTE: Each correct selection is worth one point.

SC-100 Question 27

Options:

Buy Now
Questions 28

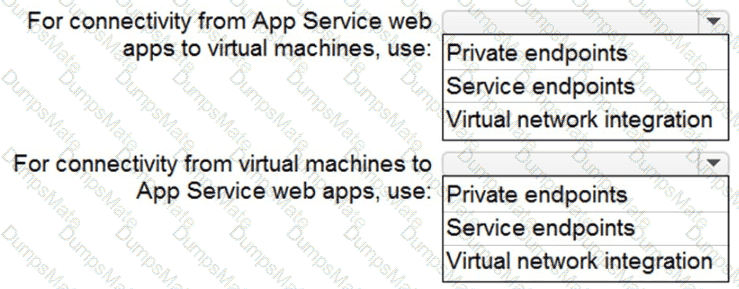
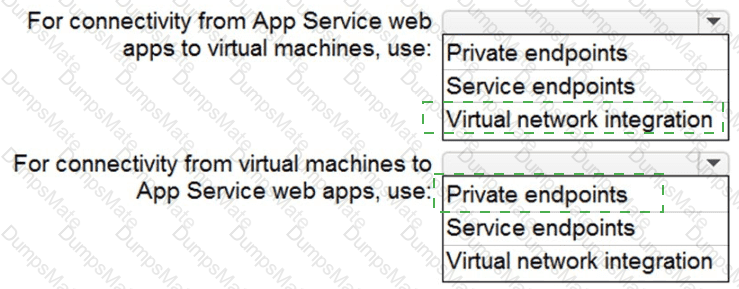
You need to recommend a strategy for App Service web app connectivity. The solution must meet the landing zone requirements. What should you recommend? To answer, select the appropriate options in the answer area. NOTE Each correct selection is worth one point.

SC-100 Question 28

Options:

Buy Now
Questions 29

You need to recommend a solution to secure the MedicalHistory data in the ClaimsDetail table. The solution must meet the Contoso developer requirements.

What should you include in the recommendation?

Options:

A.

Transparent Data Encryption (TDE)

B.

Always Encrypted

C.

row-level security (RLS)

D.

dynamic data masking

E.

data classification

Buy Now
Questions 30

You need to recommend a solution to resolve the virtual machine issue. What should you include in the recommendation? (Choose Two)

Options:

A.

Onboard the virtual machines to Microsoft Defender for Endpoint.

B.

Onboard the virtual machines to Azure Arc.

C.

Create a device compliance policy in Microsoft Endpoint Manager.

D.

Enable the Qualys scanner in Defender for Cloud.

Buy Now
Questions 31

You need to recommend a solution to meet the security requirements for the InfraSec group.

What should you use to delegate the access?

Options:

A.

a subscription

B.

a custom role-based access control (RBAC) role

C.

a resource group

D.

a management group

Buy Now
Questions 32

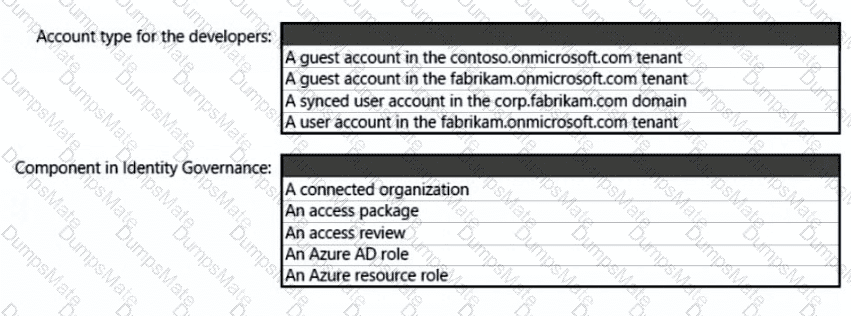
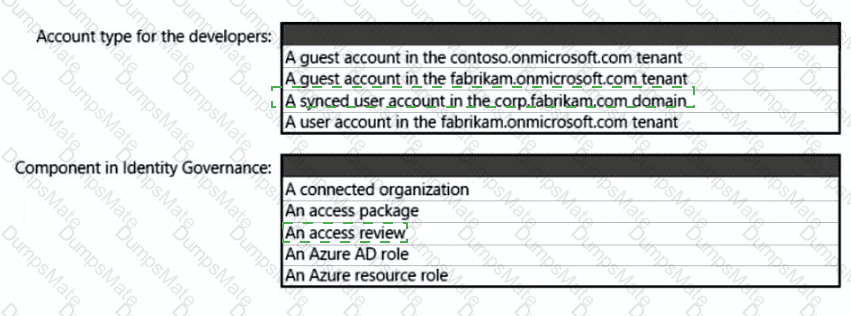
What should you create in Azure AD to meet the Contoso developer requirements?

SC-100 Question 32

Options:

Buy Now
Questions 33

You need to recommend a solution to meet the security requirements for the virtual machines.

What should you include in the recommendation?

Options:

A.

an Azure Bastion host

B.

a network security group (NSG)

C.

just-in-time (JIT) VM access

D.

Azure Virtual Desktop

Buy Now
Questions 34

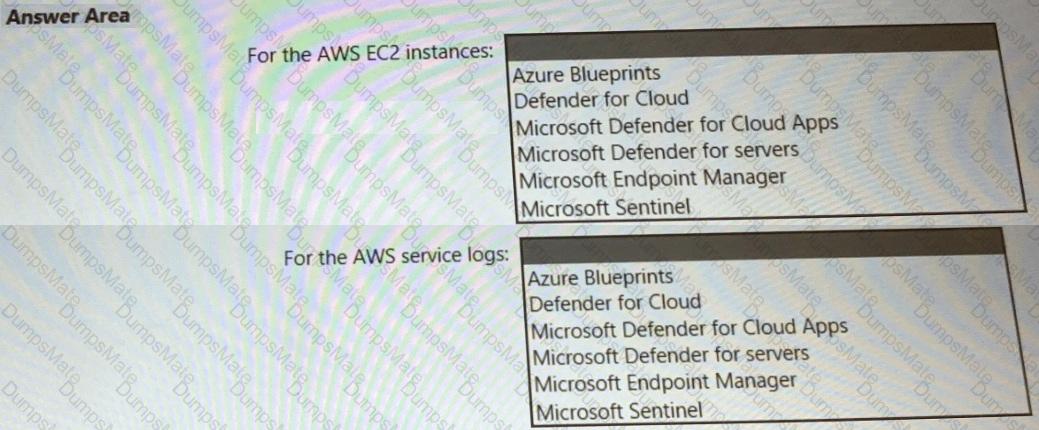
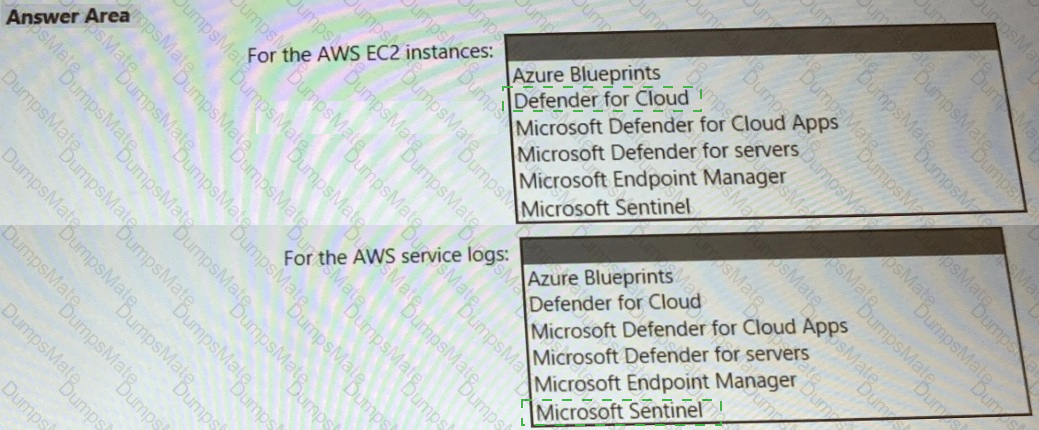
You need to recommend a solution to meet the AWS requirements.

What should you include in the recommendation? To answer, select the appropriate options in the answer area.

NOTE: Each correct selection is worth one point.

SC-100 Question 34

Options:

Buy Now
Questions 35

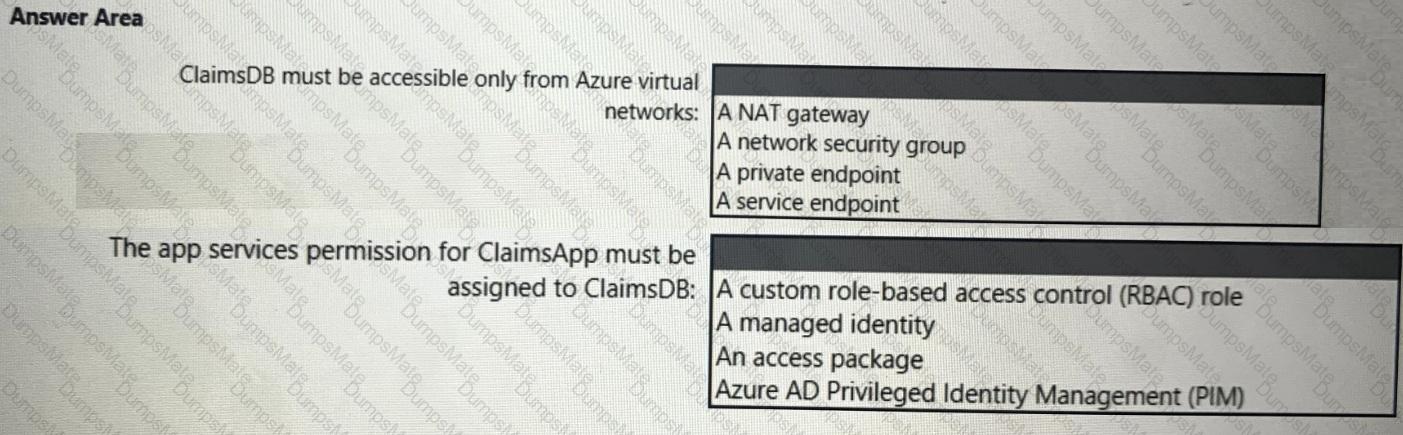
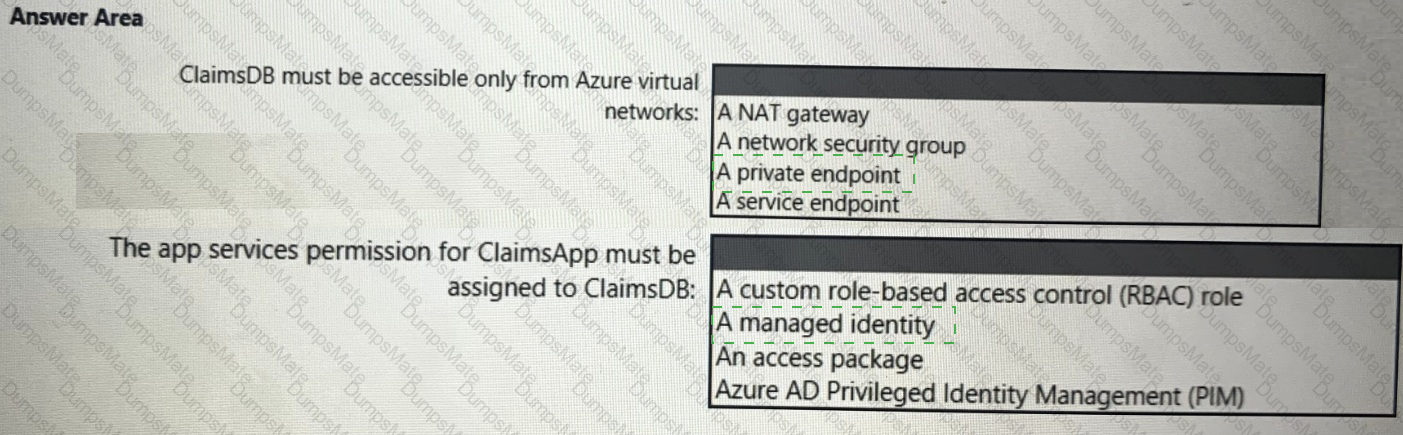
You need to recommend a solution to meet the requirements for connections to ClaimsDB.

What should you recommend using for each requirement? To answer, select the appropriate options in the answer area.

NOTE: Each correct selection is worth one point.

SC-100 Question 35

Options:

Buy Now
Exam Code: SC-100
Exam Name: Microsoft Cybersecurity Architect
Last Update: Sep 17, 2026
Questions: 344

PDF + Testing Engine

$52.5  $174.99

Testing Engine

$40.5  $134.99
buy now SC-100 testing engine

PDF (Q&A)

$34.5  $114.99
buy now SC-100 pdf
dumpsmate guaranteed to pass

24/7 Customer Support

DumpsMate's team of experts is always available to respond your queries on exam preparation. Get professional answers on any topic of the certification syllabus. Our experts will thoroughly satisfy you.

Site Secure

mcafee secure

TESTED 17 Sep 2026