Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 75only

NSE5_FWB_AD-8.0 Fortinet NSE 5 - FortiWeb 8.0 Administrator Questions and Answers

Questions 4

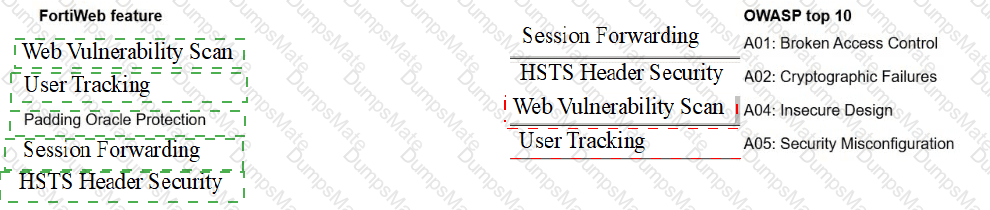
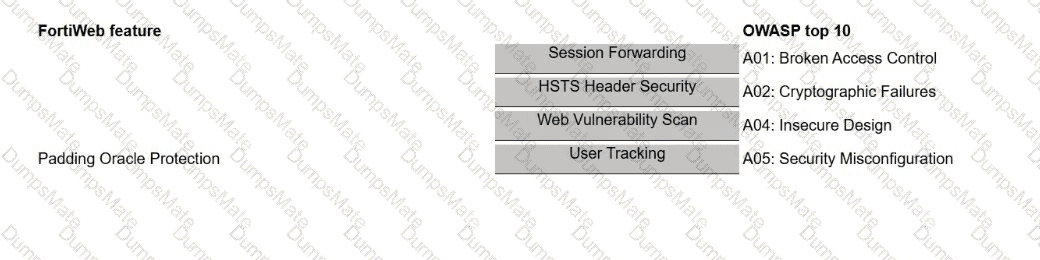
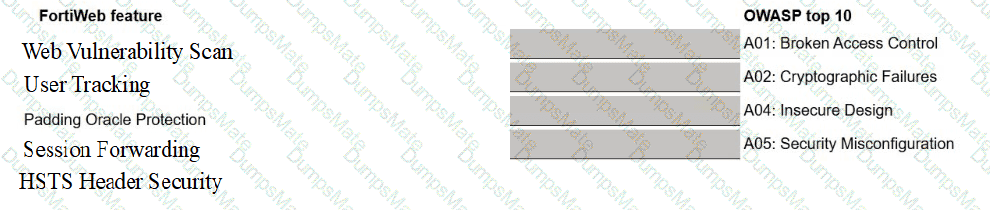
A FortiWeb administrator is reviewing issues found during a security audit. The audit lists shortcomings based on behavior, configuration, and data protection.

The administrator must break down the findings and match them with the correct FortiWeb feature.

Select each FortiWeb feature in the left column, hold and drag it to the blank space next to the OWASP issue in the column on the right. Once you match a FortiWeb

feature to the OWASP issue, you can move it again if you want to change your answer by clicking on the FortiWeb feature. You need to match five FortiWeb features to

the OWASP issue in the work area.
NSE5_FWB_AD-8.0 Question 4

Options:

Buy Now
Questions 5

A FortiWeb administrator needs to allow a known web indexer to scan the website for search engine visibility.

What is the easiest way to allow this on FortiWeb?

Options:

A.

Add the web indexer IP address to the trusted IP address list.

B.

Add the web indexer IP address to an IP exception list inside the inline protection profile.

C.

Add the web indexer IP address to the FortiGuard Known Search Engines category.

D.

Add the web indexer user-agent string to a custom signature exception rule.

Buy Now
Questions 6

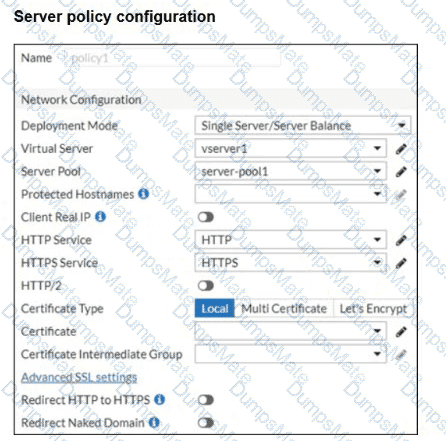
Refer to the exhibits.

NSE5_FWB_AD-8.0 Question 6

NSE5_FWB_AD-8.0 Question 6

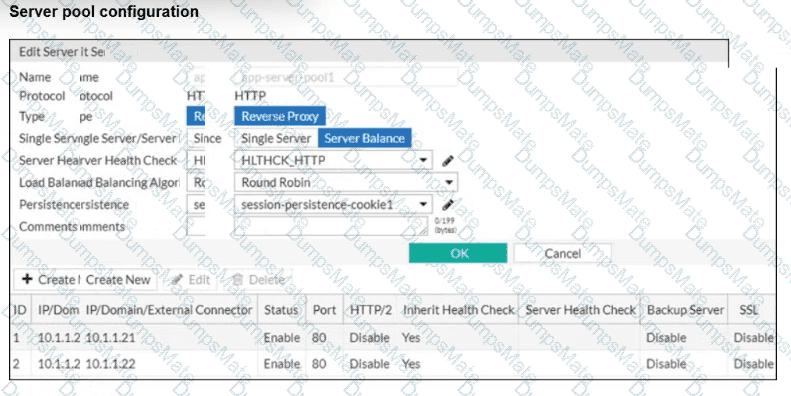
You are configuring a FortiWeb device in reverse proxy mode, placed downstream from a FortiGate. The server pool includes two back-end web servers: 10.1.1.21 and 10.1.1.22, and you’ve defined a health check policy.

After completing the server policy configuration and applying it to a virtual server, you notice that FortiWeb is not forwarding traffic to the back-end servers. No errors or health check failures appear in the logs.

Based on the configuration shown in the exhibit, which change should you make to restore back-end traffic flow?

Options:

A.

Select the correct server pool in the FortiWeb server policy.

B.

Enable Client Real IP to ensure traffic goes to the back-end servers.

C.

Change the virtual server IP address to match one of the back-end servers.

D.

Configure FortiGate to forward traffic to the back-end IP addresses directly.

Buy Now
Questions 7

A FortiWeb administrator wants to create a machine learning (ML)-based bot detection system.

Which three actions must the administrator take to build and activate this ML model? (Choose three.)

Options:

A.

Collect traffic samples for training.

B.

Verify the model manually on test data only.

C.

Apply Bayesian analysis to the model output.

D.

Build the detection model using collected data.

E.

Run the model in the live environment.

Buy Now
Questions 8

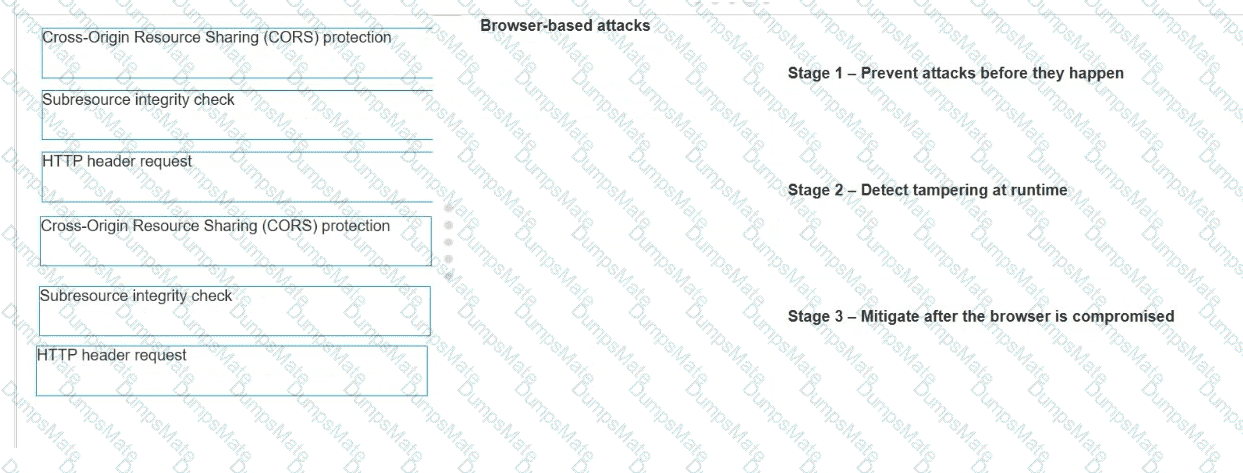
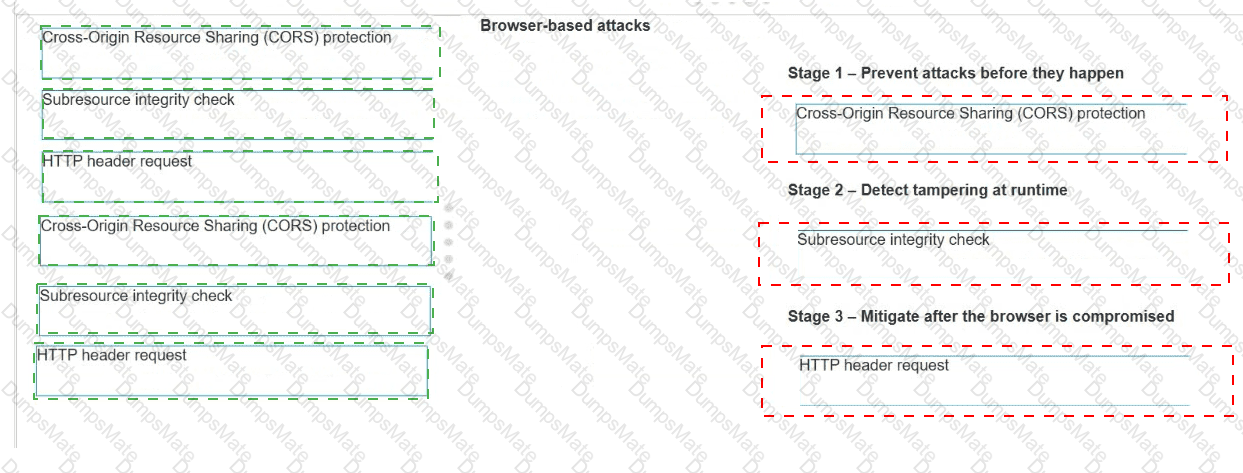
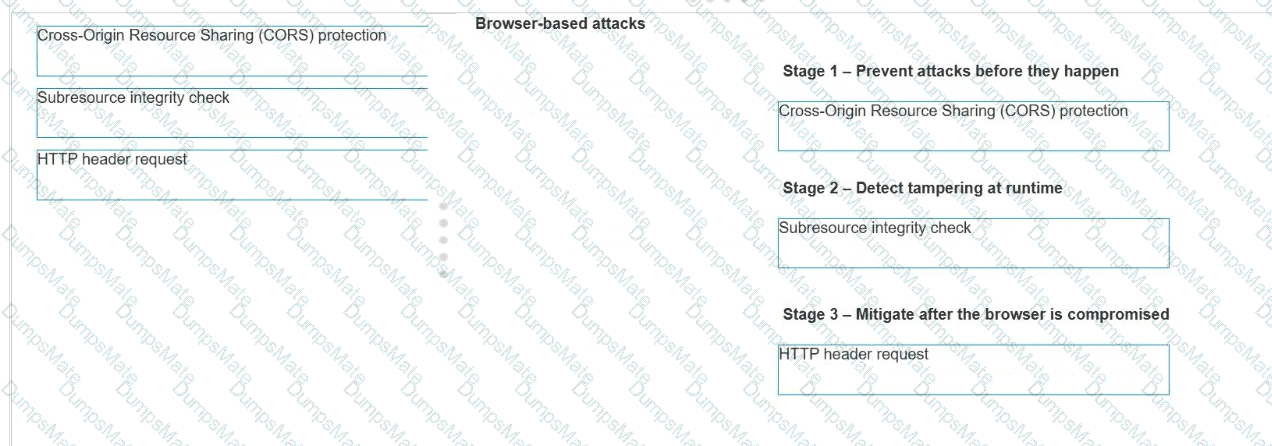
You are configuring the FortiWeb client-side protection feature to defend against browser-based attacks.

Based on the layered defense strategy, drag and drop each control to the corresponding stage of defense.

NSE5_FWB_AD-8.0 Question 8

Options:

Buy Now
Questions 9

A third-party penetration test reveals that users can bypass login controls through a mobile API. Your current FortiWeb configuration includes zero trust network access (ZTNA) profiles and cookie security, but API protection and client management are not enabled. The security team asks you to recommend the most effective way to close this gap.

Which FortiWeb adjustment would best prevent future unauthorized API access?

Options:

A.

Switch to a reverse-proxy mode to bypass cookie-based controls.

B.

Enable API protection and client management to enforce identity checks on mobile API traffic.

C.

Replace ZTNA with bot protection to reduce false positives.

D.

Log only API traffic and rely on FortiAnalyzer for future alerts.

Buy Now
Questions 10

You need to monitor and respond to repeated suspicious activity from individual users who are accessing your web application.

Your goal is to evaluate each action the user takes and apply a response when their behavior becomes risky.

What can you configure on FortiWeb to track user behavior and respond automatically when risky activity continues?

Options:

A.

Configure rate limiting on the IP reputation blocklist.

B.

Add a custom signature to block suspicious URLs immediately.

C.

Enable automatic cookie security under the server policy.

D.

Set up scoring in the protection profile to track request behavior over time.

Buy Now
Exam Code: NSE5_FWB_AD-8.0
Exam Name: Fortinet NSE 5 - FortiWeb 8.0 Administrator
Last Update: Oct 3, 2026
Questions: 36

PDF + Testing Engine

$41.25  $164.99

Testing Engine

$31.25  $124.99
buy now NSE5_FWB_AD-8.0 testing engine

PDF (Q&A)

$26.25  $104.99
buy now NSE5_FWB_AD-8.0 pdf
dumpsmate guaranteed to pass

24/7 Customer Support

DumpsMate's team of experts is always available to respond your queries on exam preparation. Get professional answers on any topic of the certification syllabus. Our experts will thoroughly satisfy you.

Site Secure

mcafee secure

TESTED 03 Oct 2026