Grab 75% Off This Black Friday: Use coupon code below to save on all exam bundles! - Ends in 0d 00h 00m 00s - Coupon code: 75only

NSE7_SOC_AR-7.6 Fortinet NSE 7 - Security Operations 7.6 Architect Questions and Answers

Questions 4

Which two statements accurately describe the process to create a new rule from a search using FortiSIEM analytics? Choose two answers.

Options:

A.

Raw event logs cannot be used for incident rule creation.

B.

The incident action is automatically configured based on the event type.

C.

All search filter rows are added into a single subpattern.

D.

The default aggregate condition will always be COUNT(Matched Events) > = 1.

Buy Now
Questions 5

Which three are threat hunting activities? (Choose three answers)

Options:

A.

Enrich records with threat intelligence.

B.

Automate workflows.

C.

Generate a hypothesis.

D.

Perform packet analysis.

E.

Tune correlation rules.

Buy Now
Questions 6

Which two statements about the FortiAnalyzer Fabric topology are true? (Choose two.)

Options:

A.

Downstream collectors can forward logs to Fabric members.

B.

Logging devices must be registered to the supervisor.

C.

The supervisor uses an API to store logs, incidents, and events locally.

D.

Fabric members must be in analyzer mode.

Buy Now
Questions 7

You configured a queue called L1 Analysts and generated shifts to cover morning, evening, and overnight shifts, with two members covering each shift.

However, you noticed that all members of the queue are assigned ingested alerts in a round-robin fashion, instead of only users who are currently on shift.

What is the problem?

Options:

A.

Shift-based assignment is disabled.

B.

The Queueable option is disabled for the Alerts module.

C.

The shift lead needs to disable automatic shift handover.

D.

The queue rules conflict with the user assignment rules.

Buy Now
Questions 8

Your company is doing a security audit To pass the audit, you must take an inventory of all software and applications running on all Windows devices

Which FortiAnalyzer connector must you use?

Options:

A.

FortiClient EMS

B.

ServiceNow

C.

FortiCASB

D.

Local Host

Buy Now
Questions 9

Refer to the exhibits.

The FortiMail Sender Blocklist playbook is configured to take manual input and add those entries to the FortiMail abc. com domain-level block list. The playbook is configured to use a FortiMail connector and the ADD_SENDER_TO_BLOCKLIST action.

Why is the FortiMail Sender Blocklist playbook execution failing7

Options:

A.

You must use the GET_EMAIL_STATISTICS action first to gather information about email messages.

B.

FortiMail is expecting a fully qualified domain name (FQDN).

C.

The client-side browser does not trust the FortiAnalzyer self-signed certificate.

D.

The connector credentials are incorrect

Buy Now
Questions 10

When configuring a FortiAnalyzer to act as a collector device, which two steps must you perform? (Choose two.)

Options:

A.

Enable log compression.

B.

Configure log forwarding to a FortiAnalyzer in analyzer mode.

C.

Configure the data policy to focus on archiving.

D.

Configure Fabric authorization on the connecting interface.

Buy Now
Questions 11

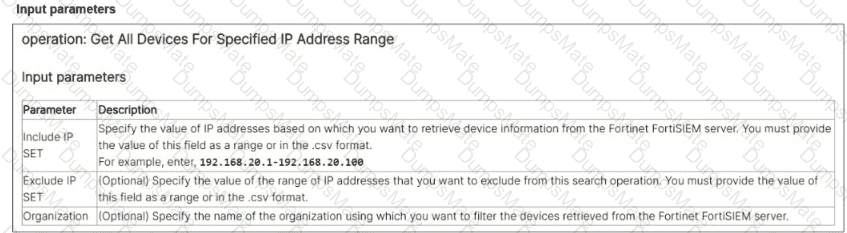
Refer to the exhibit.

NSE7_SOC_AR-7.6 Question 11

A list of FortiSIEM connector actions is shown. You want to create a playbook on FortiSOAR that allows you to accomplish the following:

Manually input a range of IP addresses.

Use the connector action in the exhibit to retrieve a list of devices from the FortiSIEM configuration management database (CMDB) within that IP address range.

For each returned result, create an asset record based on the IP address of the device.

Which combination and order of step operations fulfills the requirements with the fewest required playbook steps?

Options:

A.

1) Connector action, 2) Create record, 3) Update record

B.

1) On create trigger, 2) Connector action, 3) Code snippet, 4) Create record

C.

1) Manual trigger, 2) Connector action, 3) Create record

D.

1) Manual trigger, 2) Set variable, 3) Connector action, 4) Create record, 5) Update record

Buy Now
Questions 12

You configured a new module named Users. Next, you want to configure a playbook that creates users from ingested data. When new records are created, you want to ensure that duplicate users do not overwrite existing user records and their fields. However, you also want the playbook to continue running even if duplicates are encountered so that any non-duplicate records are still created. Which two actions fulfill the requirements? Choose two answers.

Options:

A.

Use the Stop the create process option in the Create Record step.

B.

Ensure the Users module has record uniqueness conditions configured.

C.

Configure the Execution Mode to run in parallel.

D.

Use the Do not create new record (keep existing intact) option in the Create Record step.

Buy Now
Questions 13

Refer to the exhibits.

You configured a spearphishing event handler and the associated rule. However. FortiAnalyzer did not generate an event.

When you check the FortiAnalyzer log viewer, you confirm that FortiSandbox forwarded the appropriate logs, as shown in the raw log exhibit.

What configuration must you change on FortiAnalyzer in order for FortiAnalyzer to generate an event?

Options:

A.

In the Log Type field, change the selection to AntiVirus Log(malware).

B.

Configure a FortiSandbox data selector and add it tothe event handler.

C.

In the Log Filter by Text field, type the value: .5 ub t ype ma Iwa re..

D.

Change trigger condition by selecting. Within a group, the log field Malware Kame (mname > has 2 or more unique values.

Buy Now
Questions 14

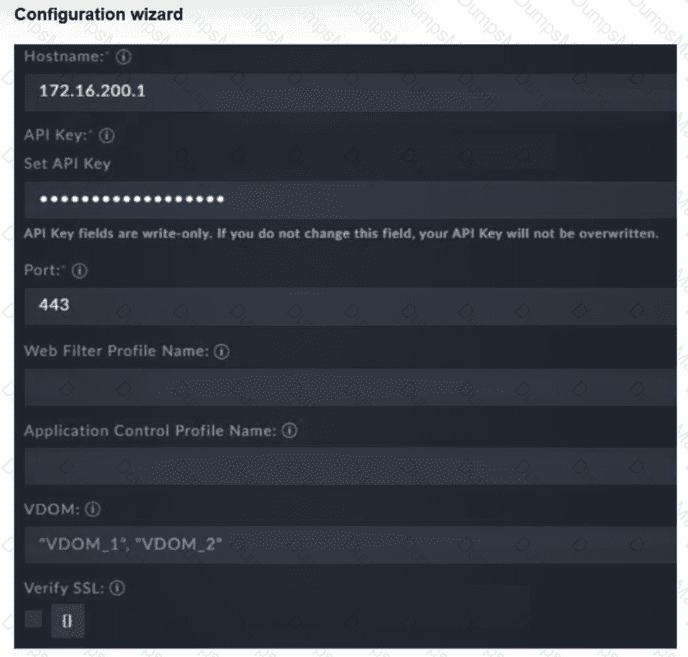
Refer to the exhibit.

NSE7_SOC_AR-7.6 Question 14

You must configure the FortiGate connector to allow FortiSOAR to perform actions on a firewall. However, the connection fails. Which two configurations are required? (Choose two answers)

Options:

A.

Trusted hosts must be enabled and the FortiSOAR IP address must be permitted.

B.

The VDOM name must be specified, or set to VDOM_1, if VDOMs are not enabled on FortiGate.

C.

HTTPS must be enabled on the FortiGate interface that FortiSOAR will communicate with.

D.

An API administrator must be created on FortiGate with the appropriate profile, along with a generated API key to configure on the connector.

Buy Now
Questions 15

You created a war room and want to run a connector action to look up the reputation of a domain. Then, you need to save the output for your team to review. However, there is a lot of output, and you want to limit the amount of information attached to the war room. How do you accomplish this? Choose one answer.

Options:

A.

From the returned output, select only the output keys you want.

B.

Apply a workspace filter to show only relevant fields.

C.

Use the Investigate tab to map only the fields you want.

D.

Lower the playbook logging level before executing the connector.

Buy Now
Questions 16

Which two playbook triggers enable the use of trigger events in later tasks as trigger variables? (Choose two.)

Options:

A.

EVENT

B.

INCIDENT

C.

ON SCHEDULE

D.

ON DEMAND

Buy Now
Questions 17

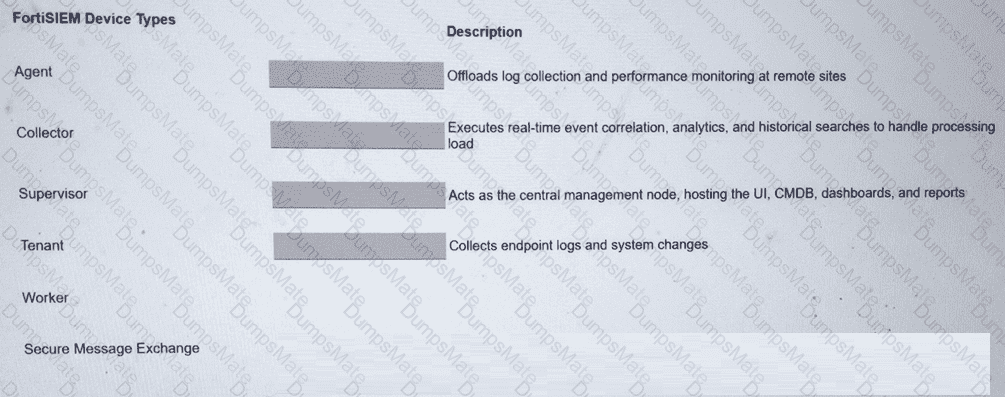
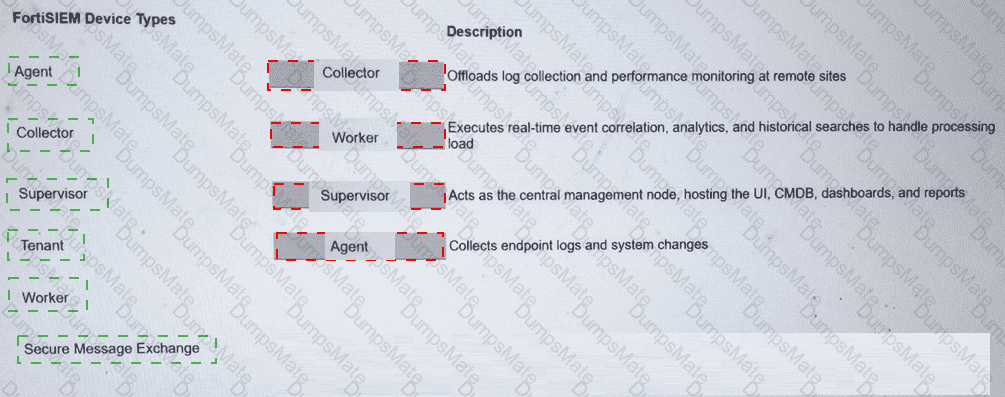
Match the FortiSIEM device type to its description. Select each FortiSIEM device type in the left column, hold and drag it to the blank space next to its corresponding description in the column on the right.

NSE7_SOC_AR-7.6 Question 17

Options:

Buy Now
Questions 18

Which three factors does the FortiSIEM rules engine use to determine the count when it evaluates the aggregate condition COUNT (Matched Events) on a specific subpattern? (Choose three answers)

Options:

A.

Group By attributes

B.

Data source

C.

Time window

D.

Search filter

E.

Incident action

Buy Now
Questions 19

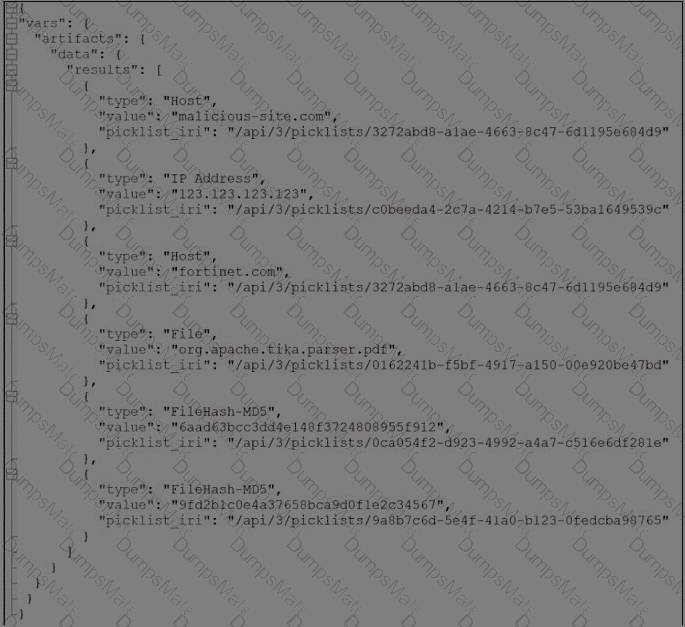
Refer to the exhibit.

NSE7_SOC_AR-7.6 Question 19

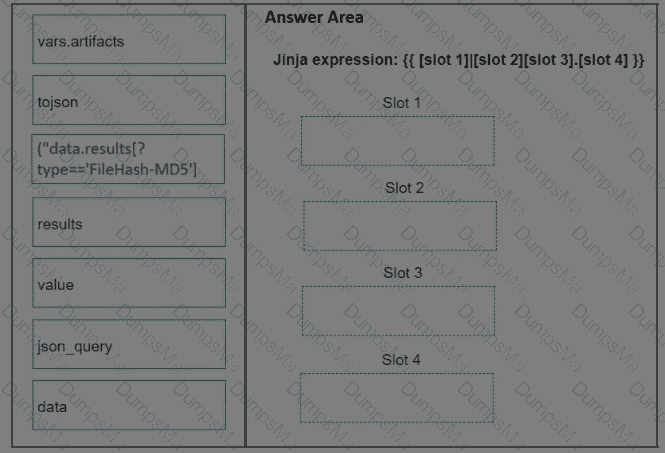
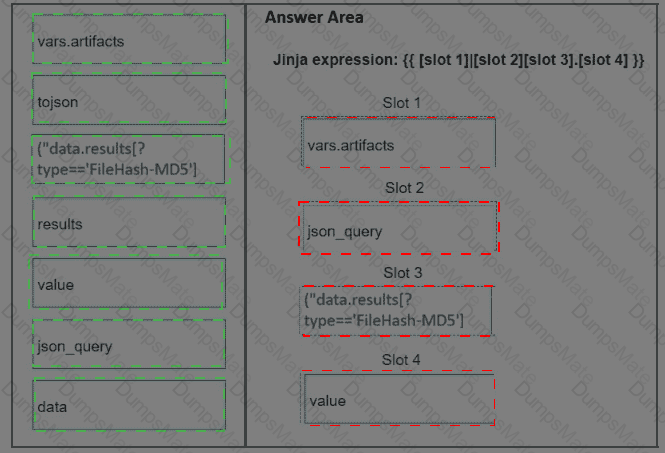
What is the correct Jinja expression to filter the results to show only the MD5 hash values?

{{ [slot 1]|[slot 2] [slot 3].[slot 4] }}

Select the jinja expression in the left column, hold and drag it to a blank position on the right. Place the four correct steps in order, placing the first

step in the first slot. Once you place an expression, you can move it again if you want to change your answer before moving to the next question. You

need to drop four jinja expressions in the work area.

Select and drag the screen divider to change the viewable area of the source and work areas.

NSE7_SOC_AR-7.6 Question 19

Options:

Buy Now
Questions 20

You want to automate a workflow on FortiSOAR so that whenever an incident is moved to the Aftermath phase, it is automatically set to status Resolved and assigned to a purple team specialist as incident lead to write an incident report. In addition, a manual task, assigned to the same specialist, will be created so they are aware of the pending work. Which three steps will accomplish this task? Choose three answers.

Options:

A.

Create a Find Record step to find matching incidents.

B.

Create a Condition step to assign both the incident and task to the specialist.

C.

Create a Manual Task step to assign the task to the specialist.

D.

Create an Update Record step to set the incident lead.

E.

Create an On Update trigger with a trigger condition that matches the Aftermath phase.

Buy Now
Questions 21

Which two types of variables can you use in playbook tasks? (Choose two.)

Options:

A.

input

B.

Output

C.

Create

D.

Trigger

Buy Now
Questions 22

Refer to Exhibit:

You are tasked with reviewing a new FortiAnalyzer deployment in a network with multiple registered logging devices. There is only one FortiAnalyzer in the topology.

Which potential problem do you observe?

Options:

A.

The disk space allocated is insufficient.

B.

The analytics-to-archive ratio is misconfigured.

C.

The analytics retention period is too long.

D.

The archive retention period is too long.

Buy Now
Questions 23

Refer to the exhibit.

NSE7_SOC_AR-7.6 Question 23

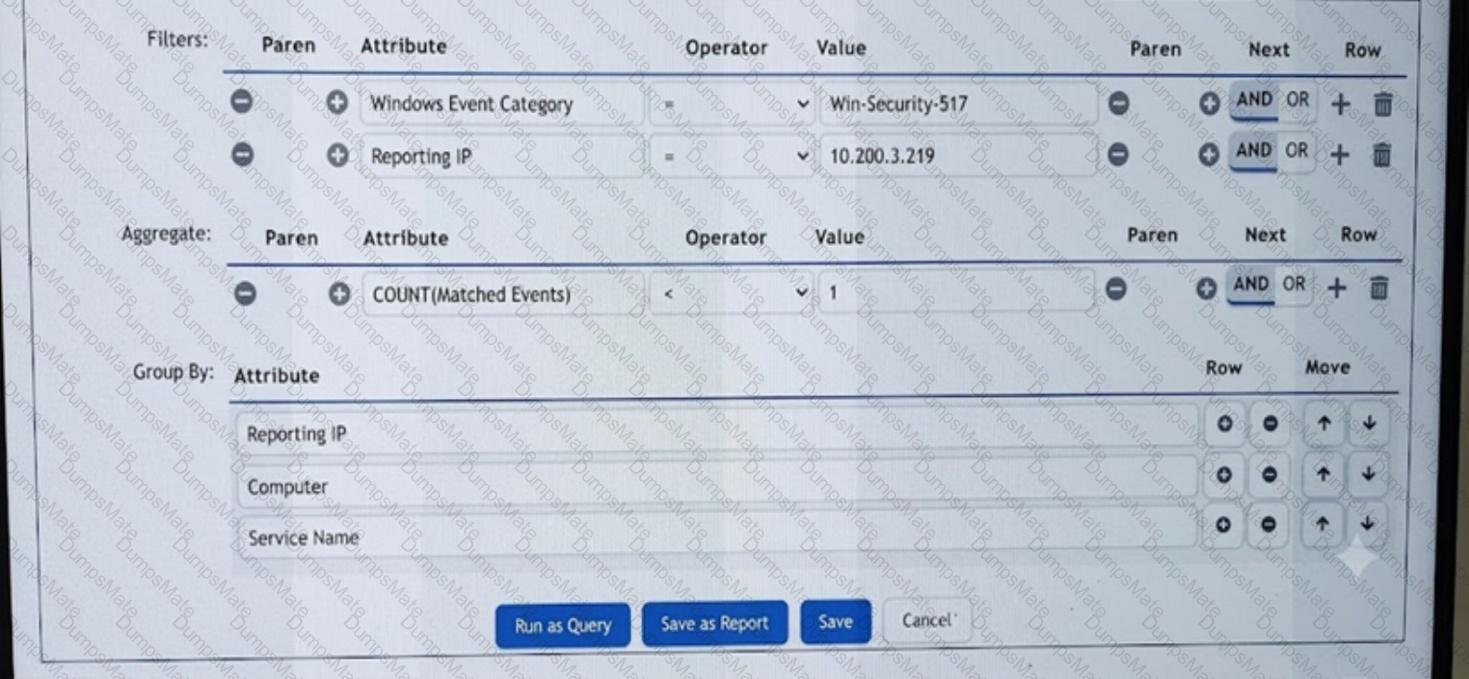
What are the two mistakes in the incident subpattern rule configuration? Choose two answers.

Options:

A.

The subpattern is missing a time window definition.

B.

The aggregate operator is incorrect.

C.

The Group By attributes conflict with each other.

D.

The mandatory Event Type attribute is missing.

Buy Now
Questions 24

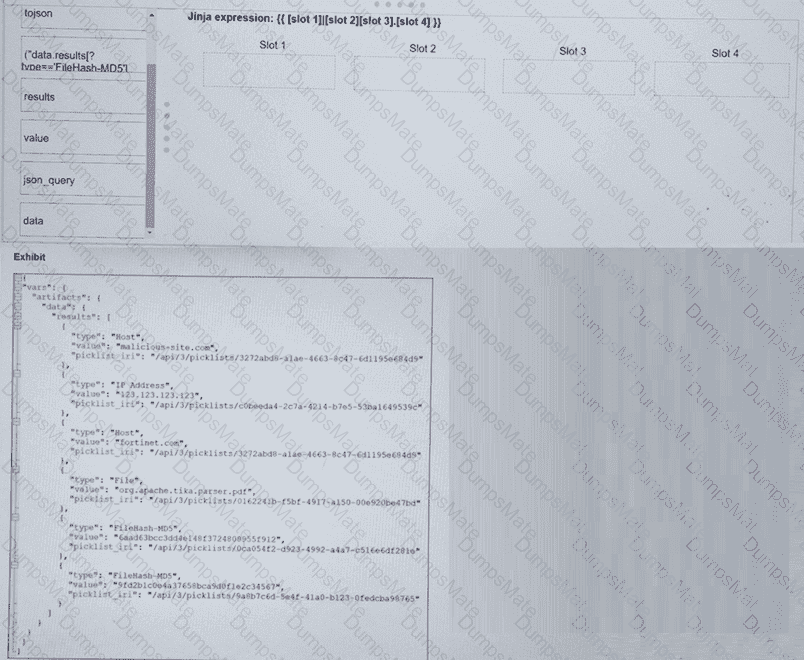
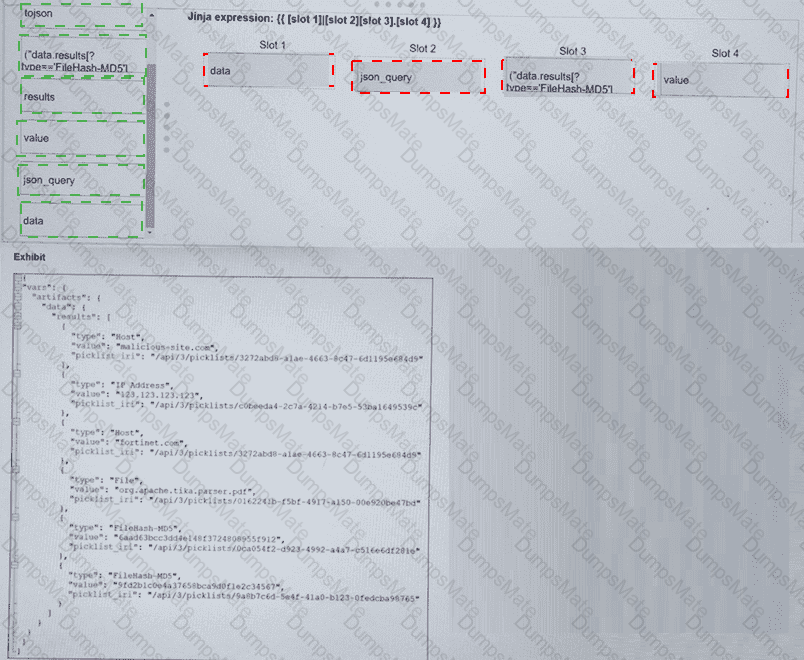
Refer to the exhibit. What is the correct Jinja expression to filter the results to show only the MD5 hash values?

{{ [slot 1] | [slot 2] [slot 3].[slot 4] }}

Select the Jinja expression in the left column, hold and drag it to a blank position on the right. Place the four correct steps in order, placing the first step in the first slot.

NSE7_SOC_AR-7.6 Question 24

Options:

Buy Now
Questions 25

Refer to this partial incident output:

Condition: if this pattern occurs within any 1800-second time window.

Host Interface Name: Red Hat VirtIO Ethernet Adapter

Recv Packet Errors: 0

Sent Packet Errors: 0

Recv Packet Discards: 37

Sent Packet Discards: 0

Recv Packet Error Pct: 0.00

Sent Packet Error Pct: 0.00

Recv Packet Discard Pct: 7.17

Sent Packet Discard Pct: 0.00

Avg Recv Interface Error: 0.00

Avg Sent Interface Error: 0.00

Avg Recv Interface Discard: 16.45

Avg Sent Interface Discard: 0.00

Which conclusion can you make about this incident? Choose one answer.

Options:

A.

It was triggered by a baseline profile incident rule.

B.

It was triggered from a FortiAI machine learning rule.

C.

It was triggered by a correlation rule.

D.

It was triggered by a lookup table.

Buy Now
Questions 26

Which two ways can you create an incident on FortiAnalyzer? (Choose two answers)

Options:

A.

Using a custom event handler

B.

Using a connector action

C.

Manually, on the Event Monitor page

D.

By running a playbook

Buy Now
Questions 27

A customer wants FortiAnalyzer to run an automation stitch that executes a CLI command on FortiGate to block a predefined list of URLs, if a botnet command-and-control (C & C) server IP is detected.

Which FortiAnalyzer feature must you use to start this automation process?

Options:

A.

Playbook

B.

Data selector

C.

Event handler

D.

Connector

Buy Now
Questions 28

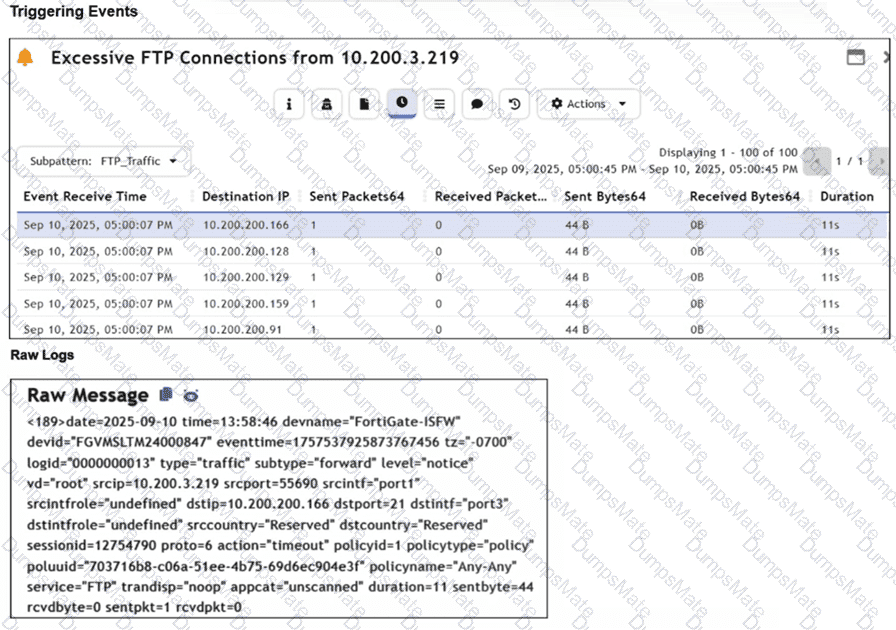
Refer to the exhibits.

NSE7_SOC_AR-7.6 Question 28

Assume that the traffic flows are identical, except for the destination IP address. There is only one FortiGate in network address translation (NAT) mode in this environment.

Based on the exhibits, which two conclusions can you make about this FortiSIEM incident? (Choose two answers)

Options:

A.

The client 10.200.3.219 is conducting active reconnaissance.

B.

FortiGate is not routing the packets to the destination hosts.

C.

The destination hosts are not responding.

D.

FortiGate is blocking the return flows.

Buy Now
Exam Code: NSE7_SOC_AR-7.6
Exam Name: Fortinet NSE 7 - Security Operations 7.6 Architect
Last Update: Nov 20, 2026
Questions: 96

PDF + Testing Engine

$42.5  $169.99

Testing Engine

$32.5  $129.99
buy now NSE7_SOC_AR-7.6 testing engine

PDF (Q&A)

$27.5  $109.99
buy now NSE7_SOC_AR-7.6 pdf
dumpsmate guaranteed to pass

24/7 Customer Support

DumpsMate's team of experts is always available to respond your queries on exam preparation. Get professional answers on any topic of the certification syllabus. Our experts will thoroughly satisfy you.

Site Secure

mcafee secure

TESTED 20 Nov 2026